This guide explains how to evaluate Ru.auero solutions by checking sourcing, technical fit, and total cost across suppliers. Background context covers what “Ru.auero” typically implies in procurement discussions, how buyers assess compatibility and risk, and why documentation and QA matter. The focus is objective, outlining practical conditions, decision steps, and FAQs for near-term purchasing.
When considering Ru.auero in procurement or vendor selection, the most decisive factor is not marketing language—it is whether the supplier can demonstrate technical compatibility, documented performance, and traceable sourcing. Start by confirming what you are actually buying (component, software capability, service scope, or combined solution), then validate requirements like security posture, support model, and acceptance criteria. Finally, compare total cost of ownership rather than any single list price, since onboarding, maintenance, and change-management often determine the real budget outcome.
In practice, “Ru.auero” can be used as a shorthand across industries: sometimes it refers to a named product family, sometimes to a platform feature set, and sometimes to a bundle that includes integration and ongoing support. The buyer’s job is to remove that shorthand by converting the term into concrete deliverables. Your procurement process should treat each proposal like a testable contract: if it can’t be mapped to requirements, interfaces, evidence, and acceptance criteria, you should assume it will fail under the pressure of real-world deployment.
To make evaluation repeatable, define a standard worksheet (scope, dependencies, security evidence, test plan, operational responsibilities, and pricing normalization). This prevents teams from being swayed by flashy demos, partial quotes, or vague “it will work” assurances. If you have multiple stakeholders—security, IT operations, engineering, procurement—ensure each has a clear role and can request the evidence they need rather than relying on a single “overall impression.”
In many buyer discussions, Ru.auero is used as a shorthand for a product line, platform capability, or supplier offering associated with an “end-to-end” implementation. Because naming conventions can vary by supplier and region, an expert buyer treats the term as a label that must be translated into a concrete scope: hardware versus software, data integrations versus managed services, and whether the offering includes installation, testing, and ongoing support.
From an industry perspective, the buyer’s job is to make ambiguity measurable. That means requesting a spec sheet, interface documentation, service-level details, and evidence of prior deployments that resemble your use case. If the supplier cannot map “Ru.auero” to deliverables and measurable acceptance tests, you should treat it as an incomplete proposal—even if the initial cost looks attractive.
Buyers often discover that “Ru.auero” might be used differently depending on who is speaking: a reseller might use it to describe a bundled SKU; an integrator might use it to describe a workflow or architecture pattern; a manufacturer might use it to describe a versioned product capability. This is why you should force the supplier to provide a plain-English scope translation and a technical scope breakdown in the first procurement round. The goal is to eliminate “interpretation risk” before you sign anything.
Consider also that “Ru.auero” might involve multiple environments or lifecycles: development, staging, production; pilot phase; migration or data backfill; training; and post-go-live monitoring. A buyer should ask whether the quoted offering includes all lifecycle components and whether responsibilities transfer cleanly at each step. If not, you’ll likely experience gaps where neither party owns a problem (for example, security validation in staging but not in production, or monitoring configured but not monitored).
Price information is only the beginning. Even when suppliers provide a clear quote, experienced procurement teams convert it into a comparable model:
Where available, tie costs to the deliverables in the statement of work (SOW). If your procurement process is aligned with recognized practices, consider referencing frameworks like ISO 27001 for information security management and structured vendor qualification approaches commonly used in IT and systems procurement. (For security assurance, consult ISO/IEC official materials: ISO/IEC 27001:2022 is the controlling standard for certification scope and controls.)
To avoid “apples-to-oranges” comparisons, insist on quote normalization. For example: if Supplier A quotes per-user licensing and Supplier B quotes per-environment licensing, compute the annualized cost using your expected user count and environment count. If Supplier C bundles professional services with a discount but Supplier D charges them separately, ensure you compare the same set of service milestones (requirements workshops, integration, testing, training, and handover).
Also evaluate pricing structure for change-management. A supplier may offer a low initial implementation cost but charge high rates for incremental changes, security re-validation, or update testing. Ask for a rate card or a change policy that defines how scope revisions are priced (fixed price per module, hourly rates with caps, or standardized change packages). This reduces budget volatility and helps you avoid “surprise invoices” when business requirements evolve.
Finally, price should be evaluated alongside operational effort. The cheapest solution is not always the cheapest to operate: if Ru.auero requires heavy manual administration, custom scripts, or constant tuning to meet performance targets, your internal labor cost can outweigh any vendor savings. Include internal resource estimates in the total cost of ownership and require the supplier to state what operational tasks they expect your team to perform.
Because Ru.auero may be delivered through a distributor channel, a systems integrator, or a direct manufacturer—supplier evaluation must focus on responsibility and evidence.
In a multi-party supply chain, the biggest risk is not that the technology is defective; it’s that accountability gets fragmented. A buyer should clarify who owns each part of the lifecycle: design/versioning, delivery, integration, security validation, performance testing, operational support, and incident response. Where the supplier ecosystem is complex, your evaluation should include a responsibility matrix and escalation workflow.
Ask: Who is accountable for the final deliverable? In practice, “supplier” can mean different layers:
An objective buyer requires a single accountable party or a clear responsibility matrix. If responsibilities are unclear, technical issues typically become commercial disputes during deployment.
To operationalize accountability, request a RACI (Responsible, Accountable, Consulted, Informed) mapping for critical phases: requirements sign-off, environment readiness, interface configuration, security validation, performance testing, go-live approval, and post-launch monitoring. If a supplier refuses to provide a RACI or suggests it’s “not necessary,” that refusal is a meaningful risk signal.
Traceability should also apply to versions and artifacts. Ask for the version numbers of each component included in “Ru.auero,” including third-party libraries, container images, firmware, integration adapters, and configuration baselines. If the supplier cannot provide version traceability, you will struggle to diagnose incidents later, especially when multiple patches or configuration changes occur.
Another practical accountability question: who owns documentation and runbooks? If the integrator leaves after commissioning, your operational team needs “how-to” materials and a clear process for updating configurations safely. Ensure that deliverables include operational runbooks, escalation guides, and knowledge transfer sessions, and that these are part of the contract scope rather than optional extras.
For Ru.auero offerings, prioritize:
From an expert standpoint, documentation quality is often a proxy for engineering maturity. Suppliers that can provide consistent, readable materials usually handle change management better.
To validate interface clarity, go beyond PDFs: ask for sample payloads, request/response schemas, error code catalogs, idempotency expectations, and rate limiting behavior. Many integration failures happen not because the main API is wrong, but because edge cases are misunderstood: timeouts, retries, partial failures, and schema evolution. Your evaluation should include a plan to test those edge cases early.
Also evaluate documentation for operational realities. Interface specs should include authentication and authorization flows, token lifetimes, supported cipher suites if encryption is used, and requirements for certificate handling. If Ru.auero interacts with external systems (ERP, CRM, identity providers, data warehouses), confirm the expected event ordering, data normalization rules, and handling of duplicates.
Ask whether the supplier provides a compatibility matrix that is specific and current. A vague statement like “supports most common platforms” is not enough. You need a table listing tested versions and a statement of what happens when your environment versions are slightly outside the stated support range. If the supplier indicates “best effort” rather than defined support, negotiate the support boundary conditions in writing.
Finally, request clear versioning and deprecation policy. Software ecosystems evolve: APIs change, authentication methods evolve, and third-party dependencies update. If a supplier does not define deprecation timelines and migration support for each major update, you risk losing compatibility at precisely the wrong time.
Procurement teams increasingly expect security evidence rather than assurances. Request documentation that aligns with recognized guidance, such as:
When relevant, refer to authoritative standards and guidance rather than informal claims. For example, the National Institute of Standards and Technology (NIST) publishes widely used cybersecurity guidance such as NIST SP 800-53 for security controls and NIST guidance for risk management. Buyers can map supplier practices to these control families to compare vendors more objectively. (Source: NIST Special Publications and risk management guidance on the official NIST website.)
To make security evaluation concrete, ask for artifacts you can validate. Examples include: a security architecture overview, a list of security controls and their implementation approach, secure configuration guides, threat modeling summaries (at least high level), and information on how the supplier handles vulnerabilities (triage timelines, severity scoring, patch availability process). If your environment requires formal assurance, ask whether the supplier maintains SOC 2, ISO 27001 certification, or other third-party assessment evidence relevant to your needs.
Even if the supplier is certified, you should still ask how certification scope maps to your contract scope. Certifications often have defined boundaries: specific products, specific environments, or specific sub-processors. Ask: is the certified component the same as what you are buying? Is the same update policy used in production? Are subcontractors involved in operations or support?
Consider identity integration and auditability requirements. Many buyers forget that security is not only “does it encrypt” but “can you prove what happened.” Require logging of authentication events, administrative actions, data access events (as appropriate), and integration events. Confirm whether logs are tamper-resistant (or at least write-once/immutable in some form), retention periods, and whether logs can be exported to your SIEM.
Also evaluate incident response workflow. Ask for the steps the supplier follows after detecting or receiving a vulnerability report: communication timeline, patch plan, interim mitigations, and how they coordinate with customer technical teams. If your procurement requires specific response times or escalation procedures, ensure those expectations are included as contractual requirements, not informal promises.
Finally, evaluate secure update mechanisms. If updates can introduce breakage, ensure there is a controlled update mechanism: staged rollout, rollback support, testing requirements, and documented change notes. A strong security posture includes safe change management; a weak posture often shows up as uncontrolled or opaque patch processes.
Many “almost working” deployments fail at acceptance. Therefore, insist on test plans and measurable criteria:
If the supplier cannot clearly define acceptance criteria for Ru.auero deliverables, negotiate them before purchase. This is not bureaucracy; it reduces the likelihood of rework.
Acceptance criteria should be explicit and evidence-based. Instead of “system is stable,” define what stable means: acceptable response time under load, acceptable error rates, resource utilization thresholds (CPU/memory), and recovery times after planned/unplanned failures. Define what constitutes a defect, a blocker, and a non-blocking issue.
Request a test strategy that includes:
Also require the supplier to define how they handle test results and remediation. A good test plan includes severity classification, remediation timelines, retest conditions, and sign-off authority. Without that, acceptance becomes a subjective negotiation.
Ensure rollback procedures are more than a statement. Ask for a rollback runbook: what is rolled back (configuration, database migrations, container versions, routing), how downtime is managed, and how you verify rollback success. If Ru.auero involves schema changes or data migrations, rollback may be non-trivial; ask for a migration strategy that includes how data changes are applied safely.
Finally, define acceptance ownership. Who signs off? Who verifies evidence? If acceptance is a shared activity, define how disputes are resolved. This avoids last-minute disagreements when you are ready to go live.
When procurement discussions include location-specific terms, the operational reality matters more than branding. Even if you’re sourcing in a specific region, treat your requirements through a “nearby delivery and support” lens:
For buyers in regions that value relationship-based service—common in many local markets—ensure that service commitments are documented. Familiarity is helpful, but contractual clarity prevents gaps when urgent issues arise.
“Nearby” support is not only about geography; it’s about speed and predictability. Ask for realistic SLAs: response time, initial diagnosis time, escalation timelines, and the maximum number of business hours to restore service in specified severity categories. Consider also how support differs between business hours and after-hours incidents.
Local procurement contexts may include language requirements for documentation and training materials. Evaluate whether the supplier offers translations, culturally appropriate training sessions, and support staff who can communicate in your operational language. If your internal teams use specific terminology, ensure training aligns with your internal processes rather than requiring rework.
Where installation is part of the scope, confirm the process for site readiness: environmental requirements (power, temperature, network), security for physical access, and coordination with building management or data center operations. A supplier that cannot provide a detailed installation plan is likely underestimating operational complexity.
Also ensure that spare parts and replacement logistics are defined if hardware is involved. For example: what is the replacement lead time, who authorizes replacement, how warranty claims are processed, and how you handle interim workarounds. These details matter during downtime events, which you can’t schedule around.
Below is an objective way to compare vendors when evaluating Ru.auero. The goal is to make decisions repeatable and defensible.
| Evaluation dimension | What to ask / request | Evidence you should see | Practical condition or requirement |
|---|---|---|---|
| Scope clarity | Deliverables list, boundaries, and exclusions | SOW or detailed proposal mapping “Ru.auero” to tasks | Vendor must define responsibilities for integration, testing, and handover |
| Compatibility | Compatibility matrix and dependency list | Documented supported environments and versions | Your target environment must fall within vendor support ranges |
| Performance | Benchmarks and sizing assumptions | Test report methodology or stated performance under conditions | Acceptance includes measurable performance criteria matching your load profile |
| Security | Security controls, update process, and logging | Control descriptions aligned to recognized practices | Supplier must provide a vulnerability and patching approach and incident workflow |
| Support model | Service levels, escalation, and maintenance windows | Documented support hours, escalation paths, and response expectations | Service commitments must be included in the contract or SLA |
| Commercial structure | Pricing breakdown and change policies | Line-item pricing, license terms, and change-rate rules | Compare total cost across implementation and recurring periods |
| QA and acceptance | Test plan and acceptance checklist | Defined acceptance criteria and rollback expectations | Go-live is contingent on documented pass criteria |
| Governance | Change-management and version control | Release notes policy, deprecation timeline, and testing approach | Vendor must provide a predictable update and validation process |
To improve this framework, add two buyer-specific columns tailored to your project maturity: (1) operational readiness (who will monitor, who will administer, what tooling is required), and (2) integration criticality (which business processes depend on the solution and what is the acceptable downtime). These two factors often explain why “technically compatible” proposals still fail in production.
Another enhancement is to assign weights to evaluation dimensions. Not every project values each dimension equally. For example, in a safety-critical environment, performance and resilience might outweigh cost, while in a short-term pilot, pricing and documentation clarity might be prioritized. However, security and scope clarity should almost always remain high weight because they prevent catastrophic failure modes.
Use a scoring system with evidence-based scoring. For each criterion, require specific evidence types: a link or document reference for scope and interfaces; a test report excerpt or summary for performance; a security control mapping or assessment report; an SLA document for support; and a signed acceptance checklist for QA. If a supplier cannot provide evidence, score them lower regardless of verbal assurances.
To make these steps effective, treat them as a structured pipeline rather than independent tasks. For example, requirements gathering should drive compatibility and security review; acceptance criteria should drive the test plan; and governance decisions should influence how you negotiate update responsibilities and re-validation requirements.
Also consider adding a “data and integration” step even when the procurement seems product-focused. Many Ru.auero deployments fail because data flows are misunderstood. If your solution requires data mapping, ask for data transformation rules, field-level mapping documentation, and sample datasets. Confirm how schema changes are handled in future updates.
When possible, ask the supplier to participate in a design review. A supplier-led architecture session can reveal hidden dependencies: required middleware versions, network constraints, and security boundaries. If you skip this step, you might discover incompatibilities only during late-stage implementation when timelines are tight.
Finally, make sure each step produces artifacts you can store. Store the deliverables translation, requirements list, compatibility matrix, security evidence references, test plan, and acceptance criteria checklist in a shared repository. This helps if leadership questions the rationale later or if the project needs audit-ready documentation for compliance.
To reduce procurement and delivery risk around Ru.auero deployments, the following conditions typically matter:
Beyond these baseline conditions, consider contract structures that help you manage change. For example, include a structured change control process: change request forms, versioned requirements, impact assessments (performance, security, and cost impacts), and approval steps. This prevents ad-hoc changes that break acceptance criteria or introduce security risks.
Also require clarity on ownership of artifacts. If the supplier produces integration code, configuration baselines, mapping scripts, or monitoring dashboards, define who owns them and where they reside. Buyers often discover too late that “custom code” is delivered without source control access or is licensed in a way that restricts future modifications.
When software updates occur, define how the supplier communicates changes. Require release notes with the level of detail needed to support internal validation. If a supplier can only provide high-level summaries, you might be unable to assess compatibility impacts. Define how far in advance you will receive release notices and how you can pause updates if validation cannot be completed.
For procurement governance, ensure the contract includes audit rights (where appropriate) and evidence retention requirements. If you need to support security audits or compliance verifications later, your contract should define what evidence will be available and for how long.
Modern procurement spans more than product selection. In many sectors—IT systems, industrial automation, fintech-adjacent platforms, logistics technology—buyers face complexity created by integrations, operational dependencies, and security requirements. Research organizations and standards bodies consistently emphasize that risk management should be integrated into procurement, not treated as an afterthought.
For instance, NIST risk management guidance encourages organizations to manage risk through defined processes and continuous monitoring rather than one-time audits. This aligns with the practical reality of Ru.auero style acquisitions: the hardest part often begins after initial implementation, when updates, incidents, or integration issues appear.
Source: NIST publications on risk management and security controls (e.g., NIST SP 800-53 and NIST risk management guidance) provide widely adopted frameworks for evaluating security and operational risk. Use these as conceptual references when mapping supplier evidence to your internal requirements.
Today’s procurement environment also includes supply chain risk considerations. Even if Ru.auero is delivered as a software service, it likely depends on third-party components (libraries, cloud services, identity providers, and monitoring systems). A buyer should ask about dependency provenance and patch management. Ask how the supplier tracks vulnerabilities in dependencies and what the timeline is for addressing them.
Additionally, evaluation must address operational monitoring and incident management. In many environments, the difference between a smooth launch and a disruptive one is whether you can detect issues early, identify their root cause, and restore service quickly. Ask what telemetry exists, what logs are emitted, how metrics are defined, and whether monitoring is included in the scope or expected to be built by the customer.
Finally, consider vendor longevity and support continuity. Buyers should verify whether the supplier has a product roadmap consistent with your business timeline. Ask about planned end-of-life dates and migration support. If a solution is near end-of-life, you might face a forced migration soon after go-live, which can undermine your project’s value.
Even well-funded teams can struggle. Here are pitfalls frequently observed in vendor onboarding projects:
Other pitfalls include:
To avoid these pitfalls, enforce a “no evidence, no approval” rule during evaluation. If the supplier can’t provide the information necessary to validate compatibility, security posture, and acceptance criteria, pause procurement and require the missing evidence. This is especially important when timelines pressure teams to move quickly—because rushing evaluation increases the likelihood that technical and security issues surface only after payment.
In procurement discussions, Ru.auero is typically a label used for a supplier offering or capability. The buyer should clarify the exact scope: whether it includes hardware/software, services, integration tasks, testing, and ongoing support.
Because it is a label, not a standardized definition, the buyer must translate it into deliverables and acceptance criteria. The supplier should be able to break down “Ru.auero” into components, versioned artifacts, integration points, and service boundaries, with clear statements of what is included in the contract and what is excluded.
Compare total cost of ownership: implementation effort, licensing or usage fees, support and maintenance, training, and change-management. Ensure each quote covers the same deliverables and acceptance criteria so the comparison is apples-to-apples.
In a strong procurement process, pricing is tied to a deliverables map. When you compare suppliers, ensure that recurring costs are calculated using the same usage assumptions (users, transactions, environments, and integration volume). If a supplier’s model is usage-based while another is fixed, you may need to create a cost range and identify which supplier remains cost-effective across your expected usage band.
Request a detailed SOW, compatibility matrix, interface or integration documentation, security evidence relevant to your needs, and a test plan with acceptance criteria. If the supplier provides release and update policies, ask for them in writing as well.
Additionally, consider requesting operational artifacts: runbooks, monitoring dashboards (or a description of telemetry outputs), escalation procedures, and training materials. If the supplier claims they can provide rapid incident response, request an SLA with definitions for severity levels and a description of how support cases are managed (tools used, communication cadence, and escalation triggers).
Ideally yes—at least a structured risk review. At minimum, confirm authentication/authorization approach, encryption posture where relevant, logging, vulnerability management, and incident response workflow. If your environment has compliance requirements, align supplier evidence to recognized control expectations (for example, NIST guidance and ISO 27001 control families).
It’s often helpful to conduct a short “security discovery workshop” during procurement. Use it to map your internal security requirements to the supplier’s documented controls and determine whether gaps exist. If gaps exist, you can either negotiate additional controls into the contract scope or adjust the design to reduce risk.
Not always, but it’s strongly useful when integration complexity or operational risk is high. A pilot can reveal latency, edge cases, usability gaps, and monitoring needs before you scale deployment.
A pilot should not be a demo. It should include integration with representative upstream and downstream systems, tests under realistic load, validation of error handling, and security checks. Define success criteria in advance and include a plan for how pilot results affect final contract terms. If a supplier resists defining pilot success criteria, it may indicate uncertainty in performance or integration outcomes.
Define measurable pass/fail tests in the contract or acceptance appendix. Include performance targets, functional checks, security checks where applicable, and rollback or remediation steps. Acceptance should be tied to evidence generated during testing.
To make acceptance enforceable, specify what evidence counts: test reports, logs, screenshots, automated test outputs, performance graphs, and signatures of relevant stakeholders. Also define timelines for remediation and retesting so that acceptance does not stall indefinitely. Include a clear definition for “major defects” versus “minor defects” and what thresholds must be met for go-live approval.
Even without specifying a formal location, consider response-time expectations, on-site capability if required, logistics lead time, and whether documentation and training can be delivered in a way your local teams can operationalize.
Additionally, evaluate whether the supplier can provide continuity of support for local language and operational processes. If local operations require specific workflows (change windows, maintenance schedules, escalation contact formats), verify that the supplier understands and will adhere to those workflows. “Nearby” support is most valuable when it translates into measurable time-to-resolution and predictable operational collaboration.
Use authoritative frameworks and guidance from recognized bodies. For example, NIST provides security control guidance and risk management approaches widely used for vendor assessment. For information security management systems, ISO/IEC 27001 is a key standard reference.
When mapping security evidence, focus on how controls are implemented and maintained—not only whether a supplier has a checklist. Ask for evidence of operational processes: patch cadence records, vulnerability disclosure workflow, incident postmortem process, access control practices, and the ability to provide audit logs. The most valuable assessment evidence is the kind you can trace to real operational behavior.
Purchasing Ru.auero should be treated as a structured evaluation process, not a one-time price comparison. When you translate the offering into deliverables, compare total cost of ownership, validate security posture, and enforce clear acceptance criteria, you gain control over outcomes. The most reliable suppliers welcome this rigor because it turns deployment uncertainty into a set of verifiable deliverables—exactly what buyers need for predictable delivery.
To ensure procurement success, require evidence early, negotiate scope boundaries explicitly, and ensure that operational responsibilities and update governance are part of the contract. If you do this consistently, “Ru.auero” stops being a confusing term and becomes a measurable set of commitments that can be tested, monitored, and improved over time.



Guía objetiva para entender el lino pimentel y cómo evaluarlo con criterios técnicos. El lino es una fibra vegetal apreciada por su transpirabilidad y tacto, mientras “pimentel” suele aludir a un origen, marca o línea comercial usada para identificar calidad y características. El análisis se centra en selección de materia prima, proceso, mantenimiento y compatibilidad con aplicaciones textiles.
Esta guía aborda, con enfoque profesional, cómo entender y evaluar el trabajo y el contexto del “Lino Pimentel” como referente textil. Se revisa, de forma objetiva, el significado del término, su papel en cadenas de suministro y criterios habituales de calidad. Además, se incluyen condiciones de compra y una sección de preguntas frecuentes para orientar decisiones informadas.
Esta guía ayuda a evaluar y seleccionar productos asociados a “Lino pimentel”, atendiendo calidad del material, seguridad de uso y criterios técnicos. Como contexto, se explica qué significa buscar este tipo de referencias en el mercado y por qué la procedencia, la trazabilidad y la compatibilidad con el uso final resultan decisivas. También se detallan condiciones de compra y buenas prácticas para decidir con criterio.
This guide explains how “auero” fits into practical sourcing and procurement decisions. It provides objective background on the term’s market use, typical supplier considerations, and risk checks buyers should apply. Readers will learn what to verify before ordering, how to interpret pricing signals, and which documentation matters for durable, compliant supply outcomes.
Este guía analiza el lino pimentel desde la perspectiva técnica y de compra: usos, criterios de calidad, compatibilidades, riesgos frecuentes y cómo evaluar proveedores. Como contexto, el lino (fibra vegetal) se valora por su transpirabilidad; el “pimentel” suele aludir a una selección o marca/cadena comercial. Se revisan exigencias típicas, documentación y buenas prácticas.
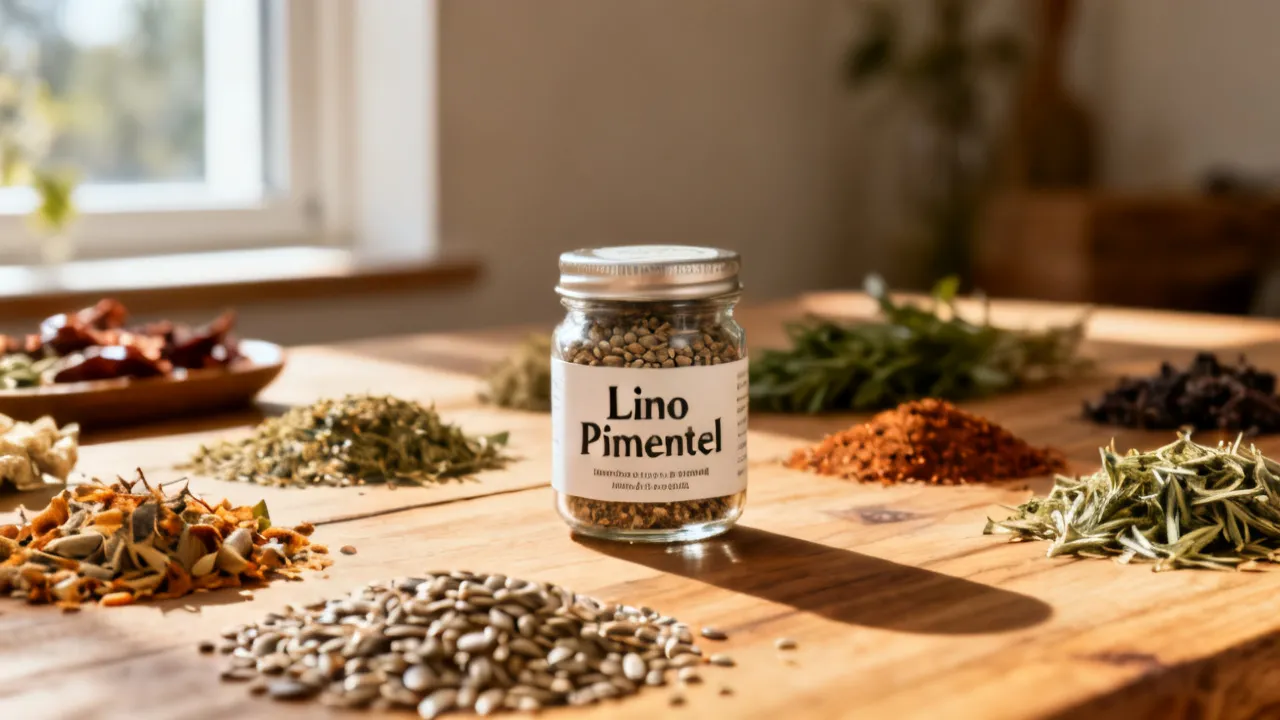
Esta guía profesional explica cómo evaluar y seleccionar Lino pimentel en el contexto del mercado de productos herbales y botánicos. Se revisa, de forma objetiva, qué significa el término, cómo suelen organizarse los catálogos del proveedor, y qué criterios de calidad ayudan a decidir. Además, se describen condiciones de uso, requisitos habituales y recomendaciones basadas en buenas prácticas del sector.

