This guide explains how to source and validate items tied to the code 055.581.671-06 with a focus on traceability, compliance, and procurement risk controls. The digits function as an identifier used in catalogs, records, or part systems, and should be verified through documentation. Background sections outline objective quality checks and supplier verification methods.
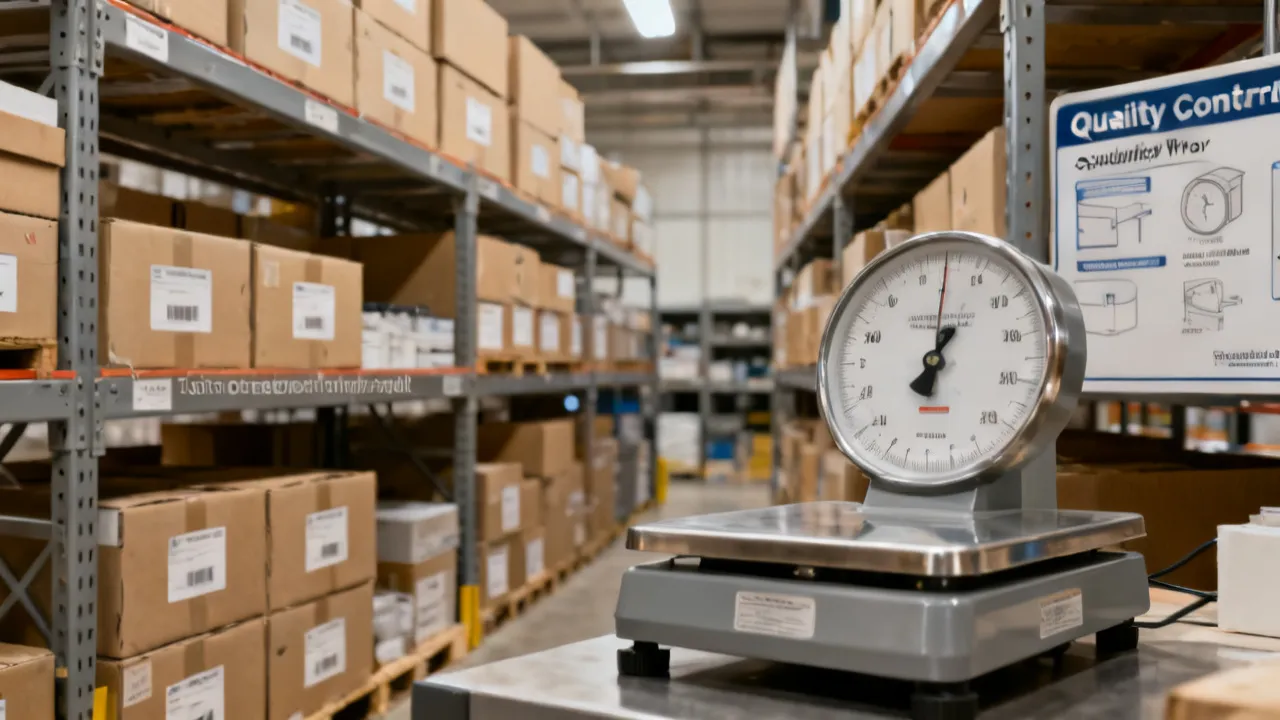
If you are procuring goods identified as 055.581.671-06, treat the code as the starting point—not the conclusion. Your procurement workflow should confirm that the identifier corresponds to the precise specification you intend to buy (materials, dimensions, tolerances, compatibility, and applicable documentation). In practical industry terms, the “same code” may still map to variants across revisions or regional labeling systems, so verification must be documentation-led and traceability-focused.
From an industry-expert perspective, the most common avoidable cost driver is not price alone—it is receiving the wrong configuration, then paying for rework, return logistics, downtime, or compliance delays. Therefore, the goal at the top of your process is alignment: confirm the code, confirm the specification, and confirm the documentation set before you commit to volume purchasing.
In many organizations, teams treat a numeric or alphanumeric identifier as a near-perfect proxy for product identity. In reality, that is only true if the identifier is managed as a controlled part number (with controlled revisions) across the entire supply chain. If it is not, then 055.581.671-06 might still exist as a stable reference in one system while the underlying configuration changes in another—especially when suppliers substitute materials, update tolerances, or bundle documentation differently over time.
To prevent this failure mode, the first “verification” step should be interpreted broadly: it is not just confirming that the label on the package reads 055.581.671-06. The proper interpretation is that you must verify the entire identity package, including revision, manufacturing lot/batch, and evidence outputs (such as CoC and test reports). When that identity package is consistent, you can treat the procurement as “like for like.” When it is not consistent, you are not merely dealing with a clerical issue; you are dealing with a traceability and quality risk.
As a practical operating principle, consider the difference between identification and qualification. Identification answers “what is the code?” Qualification answers “does this code configuration meet the requirements for my use-case?” The first step must help you answer both questions, not just the first.
When buyers talk about “the price” of a supply item, they are often referring to a unit cost. However, in supplier sourcing, the effective cost includes shipping terms, inspection effort, lead times, replacement policies, and documentation compliance. Even if you have a supplier quote for the part associated with 055.581.671-06, you should validate whether the quote is tied to the same revision and evidence package you need.
Use supplier details as a control signal. A reputable supplier typically provides:
Because you provided only the identifier 055.581.671-06 and not a specific item category (e.g., gasket, fastener, sensor, industrial component), the most objective approach is to apply a universal sourcing discipline: confirm what it is and what evidence proves it. That discipline holds across manufacturing, maintenance, and facility procurement.
It is useful to frame procurement risk in three linked dimensions:
When any one of these dimensions is ignored—especially the evidence dimension—procurement appears cheaper in the short term but becomes expensive once the failure cascades into rework, downtime, or nonconformance documentation issues.
Before purchase orders are issued, build an evidence trail. The checklist below is designed to be practical in procurement and consistent with quality-management norms (commonly used frameworks like ISO 9001 principles emphasize controlled documentation, traceability, and corrective action systems).
This is the core logic behind dependable sourcing: you reduce downstream friction by making the evidence package part of the commercial agreement. Many disputes begin because procurement and receiving treat documentation as an afterthought—something that can be collected later. In reality, for traceability-sensitive environments, evidence must be planned in advance, specified in the purchase order, and verified during receipt.
To strengthen the checklist further, consider adding internal checkpoints. For example, assign responsibility for each checklist item:
When responsibilities are clear, the risk of “everyone assumed someone else checked revision and paperwork” declines dramatically.
Suppliers vary in how they present documentation, but the consistent pattern in mature supply chains is that the evidence must be auditable. Expect documents to include references that allow you to link receipt lots/batches back to test or verification records.
Common evidence artifacts include:
Even when a supplier provides “paperwork,” your job is to ensure it is properly mapped—the identifier 055.581.671-06 should appear in a way that ties to the specific batch/lot and revision you are purchasing.
Evidence mapping deserves special emphasis because it is a frequent root cause of procurement failure. There are at least three mapping levels you may need to confirm:
In practice, some suppliers provide generic CoCs that do not specify lot/batch details. Others provide documents that reference the part number but not the revision. Either scenario might still allow acceptance in low-risk contexts, but for many industrial and regulated applications it creates an audit gap. Your procurement process should treat this as a nonconformance condition, not as a minor clerical mismatch—because auditability is itself a requirement.
Another common evidence packaging issue is when documents arrive separately from the shipment (e.g., email two weeks later) without clear linkage identifiers. If your QA system requires documents to be submitted before receiving, you must enforce that requirement. If your QA system permits post-receipt documents, you still must ensure the documents can be traced back to the correct receipt record.
When you see documentation formats that do not support traceability (e.g., scanned PDFs without searchable text, missing revision fields, or batch identifiers not clearly matched to labels), you should decide whether to reject, accept conditionally, or request re-issue. The decision should be documented based on risk and acceptance authority.
In many industrial procurement environments, identifiers like 055.581.671-06 appear in ERP catalogs, maintenance systems, supplier catalogs, and QA documentation. The risk arises when these identifiers are treated as interchangeable labels rather than as pointers to specific configurations.
From the quality-management perspective, the concept is similar to controlled document management: the buyer needs the right “version” of the item. When organizations scale purchases across warehouses or regions, identifier drift can occur—e.g., a catalog update changes descriptions without changing the code, or the supplier updates internal components while maintaining the same outward label.
To keep this discussion objective and grounded, it is useful to note that the general best practice for traceability and documentation control is widely addressed in quality systems guidance, and you can treat these principles as the standard operating logic for any code-based procurement workflow.
To make “identifier-driven procurement” tangible, consider a few real-world patterns (expressed generically to avoid assuming a particular item type):
All of these patterns connect back to the same principle: you should validate identity + evidence + revision, not just identity alone.
The table below compares how different buyers validate code-based supplies. It is framed as decision support, not as a claim that one approach always outperforms another.
| Sourcing approach | What you verify for 055.581.671-06 | When it fits | Key requirement/condition |
|---|---|---|---|
| Documentation-led procurement | Revision, CoC/test reports mapped to the code | Critical assets or regulated environments | Documents must reference the correct revision and batch/lot |
| Evidence + receiving inspection | Same as above plus agreed acceptance criteria | High variability or new suppliers | Receiving must be trained to confirm identifiers and document parity |
| Trusted-supplier program | Ongoing supplier audits and sampling plan | Repeat buys with consistent historical performance | Audit schedule and corrective-action escalation must be defined |
| Reactive replacement model | Less pre-validation, more returns/rework tolerance | Low criticality items or short-lived equipment | Return logistics and downtime cost must be acceptable |
While different approaches exist, the most robust method for 055.581.671-06 is usually the one that integrates evidence mapping into commercial acceptance criteria. The key is not which approach you choose in theory—it’s whether your process ensures that the “identity + evidence + revision” match is verified in practice.
Use this step-by-step guide to standardize how your teams handle 055.581.671-06. The structure is designed so that each step produces a decision artifact (a record, checklist, or approval) you can audit later.
Write down what “fit” means for your application: functional requirements, compatibility constraints, any performance expectations, and whether standards/regulations apply. If you skip this step, you may validate the code but not validate the functionality.
In this step, also define what “acceptance” looks like. For example, acceptance may include:
The more specific your acceptance constraints, the less likely you are to fall back on ambiguous language such as “same code” or “no issues expected.” Those phrases are useful for coordination but insufficient for compliance and quality assurance.
Request supplier documentation that explicitly references 055.581.671-06. Ensure you receive the item description, revision level, and traceability identifiers. Supplier details should be complete enough to contact the right technical owner if discrepancies appear.
To reduce back-and-forth during procurement, use a structured supplier request template. Your template can ask for:
This step is not only administrative. It is the evidence-gathering phase that enables later acceptance decisions without improvisation.
When you receive a price quote, compare the quoted item’s description, revision, and evidence package against your recorded acceptance requirements. If the quote lists 055.581.671-06 but with missing revision information, do not treat it as sufficient.
Many procurement teams focus on “line item match” in their quote review. However, the quote review should also check:
If the quote does not contain revision and evidence scope details, you should clarify those items before you place the order. The cost of clarification is usually far lower than the cost of rework, returns, and audit remediation.
Check whether CoC/test reports/material documentation are included, and verify whether they map to the correct code and lot/batch. This is where many “almost correct” shipments fail internal acceptance tests.
Evidence completeness is not just about whether documents exist. It is about whether the documents are sufficient to prove conformance for the specific delivered goods. Consider the common “almost correct” scenarios:
Your acceptance criteria should explicitly define what constitutes “complete” for your use-case. For critical supplies, you may require lot-specific certificates and relevant test reports. For lower criticality items, you might accept CoC only, but you should still enforce the code/revision mapping.
For critical supplies, agree on sampling and acceptance criteria. For lower criticality items, you may still want a basic check of identifier consistency and count/label accuracy, but the depth of testing can be scaled.
Inspection intensity is a risk-managed decision. To scale it responsibly, define criticality factors such as:
Then define the inspection plan accordingly. For example, for critical items you might specify:
In parallel, align inspection plans with supplier capabilities. If the supplier’s processes are robust and documented, you can reduce incoming testing, but only when you can reliably map evidence to delivered goods.
Commercial terms should include explicit requirements for the identifier and revision. If you cannot confirm revision, require the supplier to state the revision in writing and attach relevant documents.
At purchase order stage, your contract language matters. You can specify requirements such as:
When you embed these requirements into the PO, you reduce ambiguity and prevent “we sent the paperwork eventually” arguments. You also make it easier for receiving and QA to apply objective acceptance criteria.
At intake, verify that the received goods and documents match what you ordered: the code 055.581.671-06, the revision, and the traceability references. Record any discrepancies immediately and trigger corrective actions according to your internal policy.
Receipt verification should not be a purely visual check. It should be a structured process that includes:
When discrepancies occur, handle them consistently. A typical disciplined approach is to quarantine suspected nonconforming goods, record a nonconformance report, and engage the supplier with evidence mapping questions. This avoids the common failure pattern where goods are accepted “conditionally,” then later used without full proof—making traceability recovery much harder.
In procurement operations, disputes often originate from ambiguous requirements. To reduce those risks, align your internal and supplier expectations using clear conditions.
To further prevent disputes, it helps to standardize how your organization speaks about part identity. For example, many disputes can be prevented by prohibiting language like “it’s the same part number” and replacing it with language like “it matches the PO line’s code, revision, and lot-level evidence.”
Also, consider how you communicate “exception handling.” Suppliers often want flexibility. If you allow any deviations (for example, substitutions due to supply constraints), you should define:
When exception handling is not defined, suppliers may argue that they followed “common practice,” while you may argue they violated contract-specific acceptance criteria. Clear requirements in the PO prevent that misalignment.
In most procurement systems, a numeric identifier like 055.581.671-06 functions as a code used in item catalogs or records. However, the identifier alone does not guarantee specifications; it must be cross-checked against the item master data and revision documentation provided by the supplier.
Think of 055.581.671-06 as an index into a controlled set of product configuration data. That controlled set includes drawings/specifications, revision history, manufacturing processes (sometimes), and evidence outputs. If any of those controlled elements are missing or inconsistent, the code alone does not prove what you think it proves.
Identifiers may remain constant across catalog entries while internal revisions, materials, or packaging formats change. That is why revision control and evidence mapping are essential. Your validation should confirm both the identifier and the corresponding specification package for the correct revision.
To make this more concrete, there are multiple pathways by which “same code” can still produce different outcomes:
Any of these pathways can cause compatibility issues or compliance gaps. That is why your process should verify revision and evidence mapping, not just the code.
Price is only one variable. A buyer should evaluate supplier details such as traceability capability, documentation completeness, responsiveness during technical clarifications, and the ability to support inspections and corrective actions. These factors reduce total cost of quality failures, not just purchase price.
When you compare suppliers, consider the following cost-of-quality drivers that are often underappreciated:
These are frequently larger than the unit price difference, especially for critical items tied to 055.581.671-06.
Typically, buyers request a certificate of conformance and any relevant test reports or material documentation. The key requirement is that documents map to 055.581.671-06 and the correct revision/batch/lot for the received goods.
Because 055.581.671-06 is provided as a code without a specified item category, the exact document set may vary by product type and risk. However, the mapping principles are consistent. If a document does not clearly indicate code/revision/lot, it may not satisfy your traceability requirements.
Not always for every item and every context. However, receiving inspection is recommended for critical applications, first-time suppliers, or when documentation completeness cannot be confirmed prior to shipping. The decision should be driven by risk and acceptance constraints.
Even when you rely on documentation-led procurement, you should still ensure a baseline receiving check occurs—at minimum to confirm identity markers, counts, and evidence arrival timing. If you skip receiving checks entirely, you increase the probability that the internal recordkeeping system diverges from the actual delivered goods.
Reduce ambiguity by requiring revision level, evidence package contents, and traceability identifiers before the purchase order is finalized. Standardized request templates for 055.581.671-06 inquiries help technical teams respond faster and reduce back-and-forth.
Clarification cycles tend to happen when requirements are not explicit. A practical way to reduce delays is to set up a “pre-approved evidence checklist” for the code family you buy—so technical teams can quickly confirm whether supplier documentation is complete and correct. This is particularly useful when the supplier is asked to provide the same type of evidence repeatedly across deliveries.
Do not process the item as accepted. Record the discrepancy, quarantine the goods per your internal procedure, and initiate corrective action with the supplier. The goal is to confirm whether the mismatch is a labeling error, revision drift, or packaging mix-up—and to restore traceability.
When you initiate corrective action, ask targeted questions that restore mapping clarity:
Approach the issue as a traceability restoration task, not simply as a “wrong paperwork” task. This mindset improves resolution speed and reduces repeated mistakes.
For readers seeking established frameworks rather than ad hoc checklists, consider quality management practices and traceability principles commonly addressed in widely recognized management-system guidance. For example, ISO-style quality systems emphasize document control, traceability, and corrective action as part of maintaining consistent outputs. Additionally, supplier quality programs are often structured around audit cycles, acceptance criteria, and nonconformance handling—concepts aligned with standard procurement risk management practices.
In procurement practice, these principles translate into a few concrete habits:
Practical note: Because 055.581.671-06 is provided as a code without an associated product category in your prompt, this article focuses on universally applicable sourcing controls. If you share the product type (e.g., component category), the intended application/industry, and whether any compliance regime applies, the validation steps can be tailored more precisely.
To source and validate supplies tied to 055.581.671-06, combine code verification with specification alignment and an evidence-mapped supplier documentation review. A professional procurement outcome is achieved when the identifier, revision, and traceability records match at intake—supported by clear acceptance criteria and a corrective action pathway. When you apply this discipline, price discussions become more meaningful because you are comparing like with like.
Ultimately, the reason this discipline matters is that procurement is a downstream risk-management function. The “wrong item” problem is rarely just about receiving an incorrect physical product—it is about receiving an item whose configuration and documentation cannot be confidently traced to your requirements. When 055.581.671-06 is treated as an evidence trigger, your organization shifts from reactive correction to proactive assurance, reducing both operational disruption and audit exposure.
If you want to tighten this further for your organization, the next practical refinement is to build a repeatable internal template specifically for 055.581.671-06 purchases: a PO clause set (revision, evidence mapping, substitutions), a receiving checklist (code/revision/lot/documents), and a nonconformance decision tree (reject vs quarantine vs conditional release). Those process assets help ensure consistency across buyers, warehouses, and quality teams—so the correct configuration is achieved not only once, but every time.



Esta guía explica, de forma objetiva, qué significa “vido porno” en búsquedas en línea y cómo abordar los riesgos asociados con contenido sexual explícito, privacidad y seguridad digital. Se revisa el contexto del término, los posibles impactos para usuarios, y buenas prácticas de navegación y verificación de fuentes. El objetivo es orientar criterios y reducir daños, sin promover el consumo.
Esta guía ofrece un enfoque objetivo para comprender “vido porno”, riesgos asociados y buenas prácticas de alfabetización digital. Se revisa el significado del término, el contexto en que suele aparecer, los impactos potenciales en la privacidad, la seguridad y la salud mental, y cómo formar criterios críticos. El objetivo es informar y orientar, sin promover ni difundir contenido explícito.
Este guia apresenta uma análise objetiva sobre Jardielvieira, ajudando a entender como selecionar opções com critérios técnicos e de fornecimento. O texto contextualiza o termo no mercado, seus usos e por que a verificação de especificações, condições e suporte ao cliente deve orientar a compra. Inclui ainda uma tabela comparativa, etapas de avaliação e FAQs para apoiar decisões seguras.
Este guia analisa, de forma objetiva, como a ElidiaPeixoto pode orientar escolhas de referência e posicionamento de marca. Partimos do uso do nome como elemento identitário e de como ele pode ser comunicado em catálogos, páginas e materiais institucionais. Em seguida, detalhamos boas práticas, critérios de fornecimento, e condições para uma curadoria consistente, com foco em qualidade e confiança.
Esta guía examina, de forma objetiva, cómo se organiza el consumo y el acceso al contenido adulto en entornos digitales. Se contextualiza qué significa “Porno” desde el punto de vista cultural y regulatorio, por qué se incorporan verificaciones de edad y controles de contenido, y qué riesgos suelen evaluarse en la industria. También se revisan requisitos, condiciones y buenas prácticas para una navegación responsable.
Este guia analisa, de forma objetiva, o posicionamento e as práticas associadas a “ElidiaPeixoto”, incluindo critérios de escolha, qualidade e relações com fornecedores. Em seguida, contextualiza os conceitos ligados a marcas, atendimento e cadeias de fornecimento, permitindo uma avaliação mais segura por parte de quem procura consistência, rastreabilidade e suporte ao cliente.

