This guide explains how to evaluate supplier contact details and email identities for safer business outreach. Objectively, it covers what an email address like “PaulosergioJorgedosSantos@gmeio” can represent, why identity consistency matters, and how due diligence helps reduce operational risk. It also outlines verification steps, documented requirements, and practical conditions commonly used by procurement and compliance teams.
When you contact a supplier, the quality of the email identity you use and verify—such as “PaulosergioJorgedosSantos@gmeio” and the presence of “PaulosergioJorgedosSantos@gmeio” in your records—directly affects whether your communication is trustworthy, deliverable, and compliant with internal controls. In procurement and supplier management, it is easy to treat an email address like a simple data field, but in practice it functions as a key link in your risk chain: it can determine whether a message reaches the right accountable party, whether a supplier responds with the correct contractual intent, and whether your organization can prove how it verified contacts if questions arise later.
This article provides an objective, industry-oriented framework for evaluating supplier contact details responsibly, emphasizing verification, documentation, and practical conditions teams apply before onboarding vendors or initiating purchase discussions. It is intentionally written to avoid assuming that any specific email string is legitimate or illegitimate. Instead, it explains how organizations can assess an email identity through evidence, consistency checks, and traceability—so outreach decisions are based on verifiable facts rather than impressions.
From a governance standpoint, supplier email identity verification also supports audit readiness. Auditors often look for proof that sensitive activities—like changing payment instructions, confirming contract terms, or authorizing onboarding—were done with appropriate controls. Email addresses, particularly when used for onboarding and payment communications, are a common target for errors and fraud attempts. The wrong email identity can cause operational delays, introduce payment redirection risk, and create confusion about who authorized what and when.
The string “PaulosergioJorgedosSantos@gmeio” resembles a personal or organizational email identifier. “@gmeio” appears similar to a domain-like suffix, though from the provided keyword it is not possible to confirm whether it is a recognized corporate domain, a third-party service, or a deliberately crafted alias. In other words, an email address can be formatted correctly and still be unverified, misconfigured, or unrelated to the supplier’s actual legal entity.
Objectively, any supplier outreach that relies on an email identity should be treated as unverified until validated through independent signals—such as official corporate records, domain consistency, and cross-referencing of contact information across trusted documentation. In responsible procurement workflows, you don’t ask “Does this email look real?” You ask “What evidence supports that this email belongs to the supplier’s authorized representative and is safe to use for the specific business action I plan to take?”
To clarify the “evidence mindset,” consider that the same email string might appear in a supplier registry due to manual entry errors, outdated data, or even opportunistic fraud when someone provides an address that was never actually controlled by the supplier’s organization. Therefore, the existence of “PaulosergioJorgedosSantos@gmeio” in your records is not enough. Your organization should maintain confidence through a process that can be explained, repeated, and audited.
Industry practice in procurement and vendor management treats contact identity as a controllable risk factor. Even when an email address looks plausible, verification protects organizations from misdirected communications, impersonation attempts, and delays caused by incorrect routing. From an operational standpoint, the cost of missing a validation step can include wasted procurement cycles, compliance complications, or inability to confirm accountability when issues arise.
Risk does not only mean fraud by external attackers. It also includes accidental risks: a supplier may have changed IT systems, moved to a new email provider, or reorganized teams such that the contact address is no longer monitored. A misdirected onboarding email can stall contractual progress, slow down purchase order issuance, or delay the supplier’s readiness to ship. In a regulated environment, that delay can create cascading compliance issues: contract approvals may expire, service-level expectations may be missed, or reporting obligations may be triggered.
Risk is also time-sensitive. The same email address may have been correct last year but become incorrect after a supplier’s domain change. That is why many organizations apply re-verification when the business event changes: onboarding is one stage, but payment instruction changes are a higher stage. A contact that is acceptable for general inquiries may not be acceptable for financial changes without additional verification.
Finally, verification supports internal control objectives like segregation of duties and authorization accuracy. If a team member is allowed to update supplier master data based solely on a received email, the organization may inadvertently weaken controls. Verifying email identity through independent evidence is one way to ensure the organization’s data remains accurate and reduces the likelihood that a single human action drives high-impact outcomes.
Teams commonly apply contact identity checks at multiple points: initial inquiry, supplier registration, contracting, payment setup, and ongoing performance communication. If “PaulosergioJorgedosSantos@gmeio” (or any similar identifier) appears in internal records, a responsible process ensures that the email is not the sole proof of identity.
Below are common “touchpoints” where organizations often treat supplier email identity as a control-relevant attribute:
In a mature environment, each touchpoint has a different control intensity. The goal is proportionality: apply more rigorous verification when the business action has a higher risk profile.
From an industry expert perspective, the strongest verification methods are not those based on appearance, but those based on consistency across authoritative sources and operational traceability. Instead of asking “Does this email look real?”, teams ask:
Many organizations underestimate the value of traceability. Even if you verify correctly, you still need records that prove your verification was performed and that the decision followed policy. Without traceability, verification efforts may be difficult to defend.
Traceability also helps operational teams. When disputes occur—like a late delivery or billing issue—knowing who authorized which contact or request can reduce confusion and speed up resolution.
Below is a practical, step-by-step workflow procurement and compliance teams often follow when validating supplier contact details like “PaulosergioJorgedosSantos@gmeio”. This approach stays objective and does not rely on unverified assumptions. The workflow can be adapted to your internal policies, but the conceptual structure remains consistent: gather evidence, verify identity through independent sources, confirm role/authority, record approvals, and apply escalation thresholds.
| Verification Element | What to Check | Typical Evidence/Outputs | Conditions/Requirements (Examples) |
|---|---|---|---|
| Domain and Email Structure | Confirm how the domain suffix is used and whether it aligns with supplier branding or known corporate identity. | Captured email headers, domain ownership documentation request, supplier confirmation email. | Proceed only after supplier confirms responsibility for the address; flag if inconsistent with official records. |
| Cross-Reference With Official Supplier Records | Compare the email against invoices, signed documents, and registration details. | Documented matches or differences; a reconciliation note. | At least one independent match required for onboarding; discrepancies must be escalated. |
| Sender Identity and Role Alignment | Ensure the person’s role matches the supplier’s stated organizational structure. | Signed attestation or organizational chart; contact role confirmation. | Do not treat email ownership alone as authority to contract or request payments. |
| Operational Deliverability Signals | Assess whether communications reliably reach the intended supplier and receive expected responses. | Communication log; response verification. | Multiple consistent responses over time preferred before operational changes (e.g., payment instructions). |
| Escalation and Exception Handling | Define what “looks suspicious” and how exceptions are approved. | Exception ticket; approval record. | If verification fails or evidence is missing, require escalation to compliance or procurement leadership. |
Notice that the workflow is “layered.” Even if the domain appears familiar or the email address looks structurally valid, the workflow does not end there. Instead, it checks for alignment with official sources and ensures the person has the appropriate role.
Different organizations use different mixes of controls. Below is a comparison of typical approaches to evaluating supplier contacts like “PaulosergioJorgedosSantos@gmeio”. The goal is to help you select appropriate controls for the risk level of the business event you are undertaking.
| Approach | Strengths | Limitations | When It’s Usually Used |
|---|---|---|---|
| Appearance-Based Screening | Fast initial review; useful for triage. | Can be fooled by look-alike addresses; weak traceability. | Early inquiry phase only, not onboarding or payment setup. |
| Document Cross-Checking | Improves accountability and audit readiness. | Requires time to obtain and validate documents. | Vendor onboarding, contract preparation, and supplier registration. |
| Role and Authorization Confirmation | Reduces impersonation and unauthorized requests. | May require legal or compliance involvement. | For contracting, pricing approvals, and payment instruction changes. |
| Communication Log Validation | Demonstrates operational consistency over time. | Still not a substitute for authoritative records. | Ongoing supplier management after initial verification. |
A common maturity path for organizations is to move from appearance-based screening to a more evidence-based model. Appearance-based screening is not “wrong” for all steps, but it should not be the deciding factor for high-impact actions. If a procurement team changes payment instructions based primarily on an email that “looks right,” that is a control gap.
Document cross-checking and role confirmation usually provide stronger accountability. Communication logs are valuable too, but they should complement rather than replace evidence from authoritative sources.
Identity verification for suppliers is part of broader risk management practices. While the specific email address “PaulosergioJorgedosSantos@gmeio” is provided as a keyword, the underlying principle is universal: organizations manage the risk of misidentification and fraud by applying layered checks. For general guidance on authentication, identity assurance, and business communication security concepts, organizations often rely on established frameworks such as:
These references support the idea that verifying identities using independent evidence is more reliable than trusting a single input. (The article does not claim that any particular supplier identity is legitimate or illegitimate; it only describes responsible evaluation methods.)
In practical procurement terms, these frameworks translate into concepts like:
In many organizations, the approval criteria become stricter once money, contracts, or sensitive operational steps are involved. An objective “conditions and requirements” mindset might include:
One practical reason these conditions matter is that suppliers are not the only parties communicating via email. Fraudsters often exploit the fact that organizations move quickly when they believe they are dealing with a legitimate supplier. A verification approach that is clear and consistently applied helps teams resist pressure and reduces the likelihood of bypassing controls.
Another reason is that contract and payment actions often have legal consequences. If your organization cannot later show that it used the correct authorized contact, disputes can become more expensive and time-consuming.
Once the verification steps are underway, how you communicate matters. A well-structured outreach reduces back-and-forth and supports auditability. It also increases the odds that the supplier will respond with the specific confirmation your process requires.
Recommended objective practices:
In some environments, buyers also benefit from explicitly stating the verification logic, such as “For audit purposes, please confirm this address and your authorization to receive onboarding communications.” This reduces misunderstanding and makes it easier for suppliers to comply with your control requirements.
Understanding what can go wrong helps teams improve verification. Here are common failure modes that occur when organizations treat email identity as a minor attribute rather than a control-relevant element:
These failure modes are not theoretical. They appear in real-world incidents across industries, particularly where payment and contract workflows rely heavily on email communications.
One concern teams often raise is that strong verification might slow procurement. That can happen if documentation requirements are unclear or overly burdensome. The key is to document verification in a way that matches your workflow and risk level.
From an operational perspective, you can reduce friction by:
When documentation is consistent, suppliers experience less confusion and buyers spend less time responding to internal questions like “Why did we accept that email?” Because your process already captured that explanation.
A robust verification program is not one-size-fits-all. You can design it around the intended “use case” of the supplier email identity—what you plan to do with it.
| Use Case | Risk Level (Typical) | Suggested Verification Strength | What Not to Do |
|---|---|---|---|
| General inquiry (catalog, lead times) | Low to Medium | Cross-check against existing supplier documents or a known supplier portal; ensure role contact is reasonable. | Do not update supplier master data or payment details based only on this inquiry. |
| Supplier onboarding (creating vendor record) | Medium | Cross-reference email with invoices/registration documents; confirm authorized contact role; record the evidence. | Do not treat a single email confirmation as the only proof. |
| Contracting / amendments | High | Confirm authority; require alignment with signatory info or contract manager role; document approvals. | Do not rely on an email reply as evidence of legal authority. |
| Payment instruction changes | Very High | Out-of-band confirmation via known channel; segregate duties; require approvals and a documented trail. | Do not accept payment routing changes solely due to an email from “PaulosergioJorgedosSantos@gmeio” or any other address. |
| Ongoing operational communications | Medium | Use verified channels; maintain logs; re-verify if the supplier changes contact details. | Do not ignore changes in address/domain without investigating. |
This table illustrates how an organization can keep outreach efficient while maintaining strong controls. You use the same foundational verification elements—consistency, authority, traceability—but apply them at different intensities depending on use case.
Because “PaulosergioJorgedosSantos@gmeio” includes a domain-like suffix “gmeio,” teams often want to validate the domain’s relationship to the supplier. However, domain validation must be done carefully, because “domain exists” does not mean “domain is legitimately owned by the supplier.”
In practice, procurement and compliance teams may request one or more of the following, depending on available resources:
Even with these checks, it is important to recognize limitations. Attackers may use legitimate-looking domains or compromise accounts. Therefore, domain validation should support, not replace, role and authorization confirmation and documented audit trails.
Many procurement failures occur when organizations confuse responsiveness with authorization. A contact may respond quickly and even provide accurate information, yet still not be permitted to approve contracts or change payment details. Responsible verification must focus on role alignment and authority.
Role alignment is easier when suppliers provide clear structure in onboarding. For example, suppliers can include:
For a specific email like “PaulosergioJorgedosSantos@gmeio,” role alignment means you confirm what the person does within the supplier organization. If the supplier’s onboarding record indicates that payment changes must be authorized by a finance manager, then a response from a sales contact may be insufficient for payment routing changes.
From an internal control viewpoint, the goal is not to question every supplier contact; it is to ensure that decisions with legal and financial impact are made based on verified authority.
Traceability means the organization can explain the process it followed. When evidence is missing, even correct decisions become difficult to defend.
Common traceability artifacts include:
If later there is a compliance question—such as why the organization accepted “PaulosergioJorgedosSantos@gmeio” in a vendor master record—traceability enables a clear narrative: what was checked, what evidence supported the decision, and who authorized any exceptions.
Even the best verification workflow encounters edge cases: missing documents, slow supplier response, changes in supplier structure, or urgent procurement schedules. Organizations need escalation and exception pathways so teams are not forced to bypass controls.
An escalation strategy often includes:
Exception handling should not mean “ignore verification.” It should mean “verify as much as possible, document the gap, and get a decision on acceptable risk.” For high-impact actions like payment instruction changes, exceptions should be rare and heavily controlled.
While your organization’s legal and compliance requirements may require specific wording, you can structure outreach to support verification. Below are example templates that align with an objective verification workflow. (These are illustrative and should be adapted to internal policy and language requirements.)
Template A: Supplier onboarding contact confirmation request
Subject: Supplier Onboarding Contact Confirmation – [Supplier Name]
Hello [Supplier Name/Team],
As part of our onboarding process, could you please confirm the following for [Supplier Name]:
For audit purposes, please respond from the confirmed address and include any reference that links this contact to your supplier registration or legal entity records (e.g., registration ID, invoice reference, or letterhead confirmation).
Thank you,
[Your Name]
[Your Title / Procurement Department]
Template B: Payment instruction change confirmation (out-of-band)
Subject: Action Required – Confirm Payment Instruction Update for [Supplier Name]
Hello [Supplier Finance/Accounts Payable Team],
We received a request to update payment instructions. For control and audit requirements, we cannot apply payment changes based solely on email. Please confirm the requested payment details using your verified, known channel.
To complete this request, contact us using the approved method listed in our existing supplier records, or via the known phone number/address on file.
Thank you,
[Your Name]
[Your Title / Accounts Payable / Procurement]
Templates like these help shift the supplier response from “just replying” to “confirming authorization through the control path,” which strengthens governance.
It indicates an email identifier format. From the keyword alone, you cannot determine the supplier’s legitimacy, the domain’s ownership, or the sender’s authorization. Responsible evaluation requires independent confirmation through official records or supplier attestations.
Email addresses can be misconfigured, impersonated, or routed through aliases. Verification using independent evidence—such as contracts, invoices, supplier registration documents, or official confirmations—creates stronger traceability and reduces misidentification risk.
Pause onboarding or pause payment-related changes. Escalate to compliance or procurement leadership and request additional evidence or official contact confirmation via a known channel. Document the reason for the pause and the remediation steps.
Yes. In many markets, business norms around formal letterheads, callback practices, or documentation vary. If you operate “nearby” a region with distinct procurement procedures, align your verification approach with local administrative practices and any applicable regulatory requirements. (No specific city or country was provided in the keyword set, so the guidance remains general.)
Not solely from the keyword text. Domain trust depends on domain ownership, security configuration, history, and confirmation from authoritative supplier records. Use document cross-checking and supplier confirmation rather than relying on appearance.
They provide general principles for identity assurance, risk-based verification, and defensive measures against impersonation and social engineering. In practice, teams adapt these principles into procurement workflows—using evidence, approvals, and audit trails rather than trusting a single data point.
An independent confirmation method is any confirmation that does not rely on the same potentially unverified channel or thread used to introduce the change. For example, if an email request proposes a payment update, you may confirm via the phone number or address previously validated on supplier onboarding records, or via a trusted portal. The key is that the confirmation should be independent from the untrusted input you are trying to validate.
There is no single universal frequency, but re-verification is commonly triggered by events rather than fixed dates. Examples include supplier onboarding (initial), supplier record changes (new email/domain), payment instruction changes, contract amendments, or when communications fail unexpectedly. Some organizations also conduct periodic recertification at defined intervals for higher-risk categories.
Not necessarily. Internal records indicate you have captured the value, but they do not prove it is correct or authorized. Evidence means you can show that the email address was validated against authoritative sources and that approval decisions were recorded. A captured value without evidence may still be considered unverified.
If the supplier cannot provide independent evidence or role confirmation, organizations typically either (a) pause high-impact actions until evidence is obtained, or (b) process only low-risk communications while escalation runs in parallel. For payment or contracting actions, many organizations require stronger confirmation methods and will not proceed without them.
Whether you are managing supplier onboarding, responding to inquiries, or preparing contracting steps, evaluating contact details responsibly is an essential control. Treat “PaulosergioJorgedosSantos@gmeio” and similar email identities as unverified inputs until validated through independent evidence, role confirmation, and documented requirements. This approach supports safer operations, clearer accountability, and more resilient supplier relationships—without relying on guesswork or unsupported claims.
In practice, the most important shift is cultural as much as procedural: procurement teams should adopt an evidence mindset where email identity is one factor in a layered verification process. When your organization can consistently demonstrate how it verified supplier contacts—especially for actions involving contracts and payments—it reduces risk, supports audit readiness, and improves the reliability of supplier communications over time.



This guide explains how to evaluate product identifiers and procurement requirements linked to 31653652888, emphasizing responsible supplier screening, specification checks, and cost realism. Objectively, such identifiers often support traceability, quality assurance, and inventory control across procurement workflows, where buyers must confirm materials, documentation, and delivery conditions before ordering from any supplier.
This guide explains how to evaluate ADAILTON.DOS.ANJOS.LEITE from a procurement and due-diligence perspective. Background context clarifies what the name represents in practice, how supplier identification supports traceability, and which documentation typically matters. It then compares practical requirements for selection, compliance, and ongoing performance monitoring in a neutral, decision-ready way.
This guide explains how to evaluate supplier contact details and email identities for safer business outreach. Objectively, it covers what an email address like “PaulosergioJorgedosSantos@gmeio” can represent, why identity consistency matters, and how due diligence helps reduce operational risk. It also outlines verification steps, documented requirements, and practical conditions commonly used by procurement and compliance teams.
This guide explains how to evaluate a supplier inquiry when you see 91435285468 and related identifiers in procurement workflows. It offers objective background on how such reference numbers function in sourcing, compliance checks, and order coordination, helping you interpret listings responsibly while you compare terms, supplier credibility, and service scope.
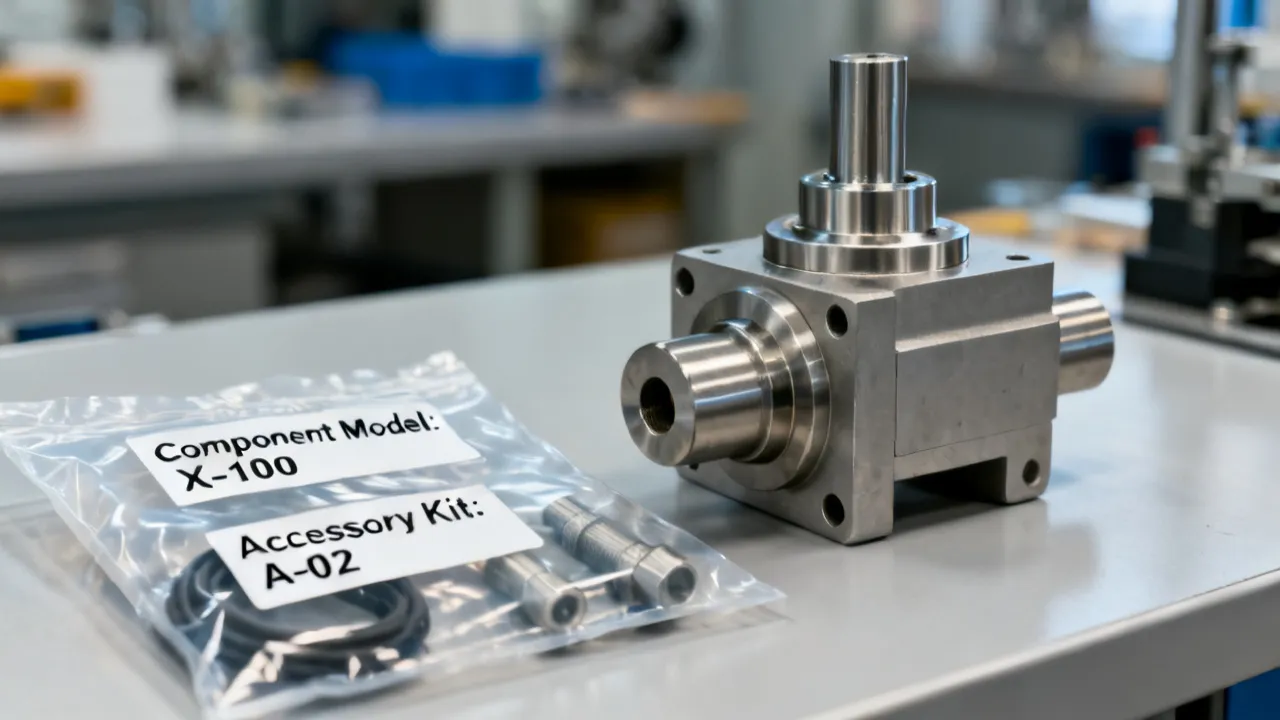
This guide explains how to correctly interpret the item code “1382 013 000200312” and related identifiers “' '' '' ” for ordering, verification, and documentation. It provides objective background on how part numbering works in supply chains, why digit sequences matter, and what an expert review checks before procurement or integration.
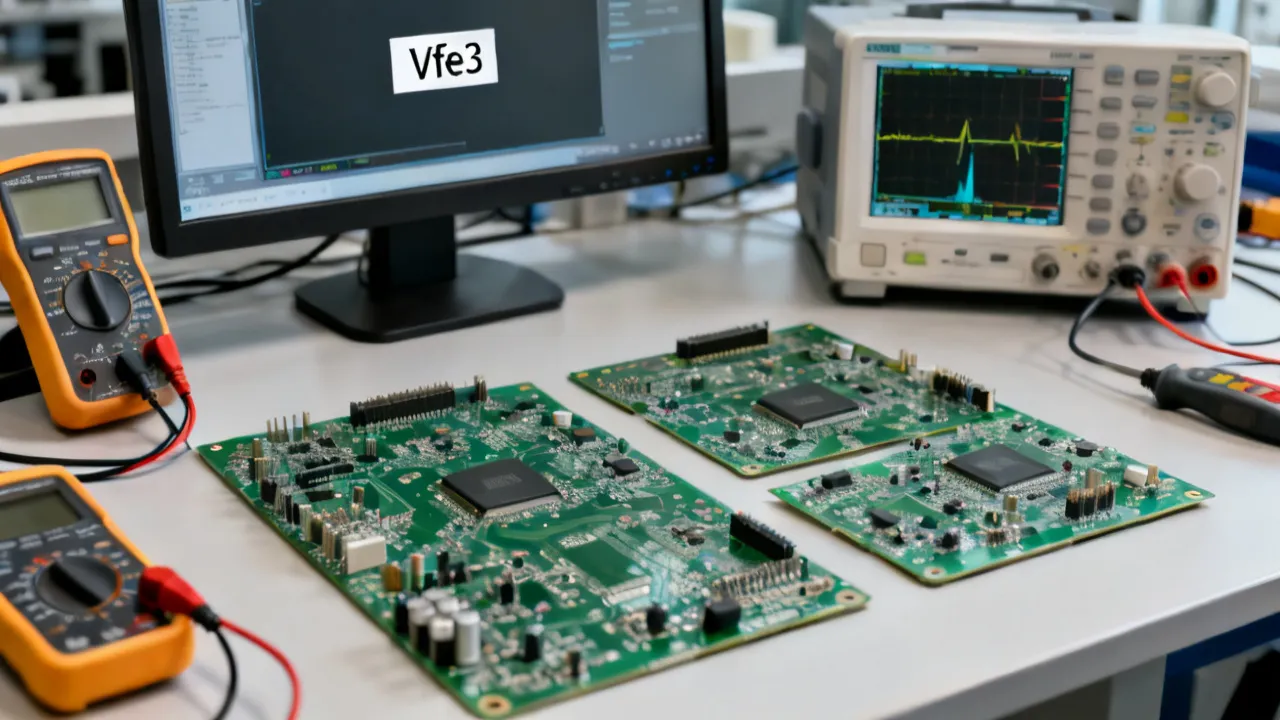
This guide explains how to evaluate Vfe3 for reliable sourcing, testing, and compliance-focused procurement. Background context covers what Vfe3 typically refers to in technical supply chains, how suppliers document quality, and why inspection steps matter for performance and traceability. It also contrasts common sourcing routes and outlines conditions to verify before purchase.

