This guide explains Cxxxvldlo from a procurement and compliance perspective, focusing on how buyers evaluate suppliers, interpret pricing, and verify documentation. Background context is provided in an objective tone: the role of vendor qualification, typical risk controls, and why consistent standards matter when keywords like Cxxxvldlo and Cxxxvldlo-related requirements appear in real sourcing activities.
Cxxxvldlo should be treated as a structured sourcing and compliance concept rather than a standalone product label. When buyers encounter terms such as Cxxxvldlo in procurement workflows, the practical goal is usually the same: confirm whether the supplier’s process, documentation, and pricing logic meet the buyer’s risk and quality requirements.
From an industry standpoint, the most important action early in any evaluation is to align three elements—(1) what Cxxxvldlo refers to in your specific contract or specification, (2) how pricing is built and audited, and (3) what evidence the supplier can produce to demonstrate compliance. This approach reduces delays, prevents rework, and supports defensible purchasing decisions.
In practice, procurement teams often lose time when they treat the keyword as something to “decode” rather than something to “operationalize.” Operationalizing means converting the term into concrete deliverables, acceptance criteria, and verifiable proof. The more ambiguous the keyword appears, the more the buyer should invest in evidence mapping, documentation controls, and explicit assumptions. Done correctly, Cxxxvldlo becomes a mechanism for consistency: it standardizes how vendors respond, how internal teams assess submissions, and how decisions hold up during internal review or external scrutiny.
Because many procurement organizations operate under auditability expectations (internal audit, compliance, regulators, customer requirements), the buyer’s sourcing process must generate an audit trail. The audit trail is not just for the final contract; it includes the rationale for why one supplier was selected, why certain documents were considered “sufficient,” and how pricing was normalized to ensure fairness. When those elements are aligned to Cxxxvldlo, the sourcing decision is not only faster but also more defensible.
In real-world procurement, buyers rarely evaluate only “cost.” They evaluate cost relative to reliability, traceability, and documentation quality. Keywords similar to Cxxxvldlo commonly appear when:
Even when the term itself is internal jargon, the buyer’s intent is usually external: ensure the supply chain can withstand scrutiny. That’s why the evaluation process should remain evidence-led, not assumption-led.
It is also common for terms like Cxxxvldlo to surface when multiple internal functions use shorthand. For example, engineering might refer to a “validated process state,” quality might refer to “documented compliance,” and legal might refer to “contractual acceptance readiness.” Procurement sees the keyword in an email chain or a requisition template, and the risk becomes that each function imagines a different meaning. The antidote is a structured interpretation step: explicitly translate the keyword to the requirement lines in the contract or specification, and document the translation.
In many organizations, procurement workflows incorporate standardized checklists, and the checklist labels might include placeholders like Cxxxvldlo. As a result, vendor responses may include attachments that the supplier believes satisfy the keyword. Unfortunately, suppliers often submit a “bundle” of documents without clearly linking each document to each requirement line. Therefore, procurement teams should plan for a linkage step: validating that the evidence actually supports each relevant requirement, not just that the evidence exists.
Finally, keywords like Cxxxvldlo can appear more frequently in categories that are sensitive to quality drift and documentation gaps—such as components used in regulated environments, services requiring controlled procedures, or deliverables where substitution or process deviation carries meaningful downstream consequences. In those settings, the buyer’s real objective is risk containment across time: ensuring that the supplier maintains the same controls not only at the start of production but throughout the contract term.
Pricing comparisons become misleading when the quotes are not framed consistently. In Cxxxvldlo-related sourcing, pricing typically includes components such as:
An expert procurement view is to demand a pricing breakdown aligned to the same work breakdown structure used in the requirement document. If Supplier A bundles compliance evidence costs into the unit price while Supplier B itemizes them, you can’t fairly “win” on spreadsheet comparisons until you normalize the quote structure.
Beyond normalization, buyers should also clarify the pricing “rules of interpretation.” For example:
When procurement fails to clarify these interpretation rules, the buyer may select the lowest unit price but later discover that critical activities are billed as “extras.” That discovery can lead to delays, disputes, and incomplete compliance evidence delivery. Therefore, procurement should request pricing terms that separate:
Another frequently overlooked item is how overhead costs interact with volume. A supplier may quote a lower unit rate at higher volumes because compliance tasks scale efficiently, but the supplier might still require full documentation completeness per batch. Conversely, a supplier may quote a higher unit rate but provide stronger evidence control, reducing buyer time spent on document chasing. In Cxxxvldlo-related sourcing, buyer total cost of ownership (TCO) should incorporate not only invoice totals but also internal labor and downstream risk costs.
To ensure comparability, procurement teams can implement a “quote translation” step. Translate each supplier’s response into a normalized format: list the deliverables, associate each deliverable with a requirement line, then associate the deliverable with a cost category. When suppliers cannot provide the breakdown, procurement should treat that as a risk signal and ask for clarifications before award.
When buyers reference keywords like Cxxxvldlo, they are commonly trying to secure evidence that the supplier has a controlled, auditable process. The best due diligence programs focus on:
It is common for supplier submissions to be “story-heavy” and “evidence-light.” A disciplined approach uses objective artifacts: calibration records, inspection reports, certificates of conformity, change-control logs, and documented corrective actions.
Evidence quality is not simply a question of having documents. It is also a question of whether the documents are:
Procurement due diligence should also consider how evidence is managed under stress. For example, during production disruptions, suppliers often revert to informal processes unless they have strong document control discipline. Buyers can probe this indirectly by asking how evidence is handled when:
Another due diligence angle is whether the supplier can demonstrate evidence for similar past work, not only for the current contract. If a supplier has performed the same scope previously, they can show redacted sample records that align with the requirements. Procurement teams should treat this as a pragmatic step: evidence from comparable work reduces uncertainty because it demonstrates operational reality rather than theoretical compliance.
Where appropriate, buyers can also review the supplier’s internal audit and corrective action history. For Cxxxvldlo-related sourcing, what matters is not the absence of nonconformities; nonconformities happen. What matters is the effectiveness of the supplier’s corrective and preventive action system: identification of root causes, effectiveness checks, and prevention of recurrence.
Finally, supplier due diligence should be proportionate. High-criticality scopes warrant deeper review, including site visits or remote audits. Lower-criticality scopes might focus on evidence mapping, document sufficiency checks, and reference checks. Still, even in lighter regimes, the buyer should maintain a clear evidence standard: every requirement should have a documented proof point.
Without assuming what Cxxxvldlo means in your organization, you can still apply a universal method: map the term to requirements, then map requirements to proof. The goal is to create a traceable link from buyer requirements to supplier evidence.
Industry-leading procurement teams typically require these risk controls (adapt as appropriate to your industry and contract):
This is how Cxxxvldlo becomes operational—turning ambiguous terminology into measurable compliance.
To expand this method into a practical risk framework, procurement can separate risk into three categories:
Cxxxvldlo-related procurement often fails when only conformance risk is considered. For example, a supplier might deliver products that appear acceptable but cannot produce the required traceability documents. In that case, the evidence risk becomes the dominant risk. Similarly, a supplier might provide excellent documentation in early batches but later shift processes without proper notifications, creating continuity risk. Therefore, procurement should ask not only “Is it correct?” but also “Can you prove it?” and “Will you keep proving it consistently?”
Specification mapping is central to controlling these risks. The buyer’s mapping table should include columns for:
If a supplier cannot provide evidence references before award, procurement can consider conditional acceptance: define which documents are mandatory for first delivery, which can be delivered later, and which must be available before final acceptance. However, the buyer should avoid “moving the goalposts” by ensuring that mandatory evidence for acceptance is not postponed beyond the acceptance decision point.
Ongoing verification should also be defined in contractual terms. Instead of a vague statement like “supplier will maintain quality records,” the buyer should specify review cadence (e.g., quarterly document updates), triggers (e.g., change notifications, deviations), and review scope (e.g., batch traceability sampling, calibration review). Doing so improves operational reliability and reduces disputes over what “review” means.
Procurement and quality professionals often rely on established management-system approaches. While the specific details vary by sector, the logic is consistent: supplier performance should be traceable, auditable, and reproducible across time.
For evidence-based evaluation, many organizations reference internationally recognized standards and guidance. For example, ISO management-system concepts emphasize documented processes, internal audits, corrective actions, and management review. For quality and traceability in regulated supply chains, quality guidance from recognized regulators and standards bodies can support contract expectations.
Reference pointers (for deeper reading): International Organization for Standardization (ISO) management system standards and related guidance documents; and quality/regulatory guidance issued by relevant government or industry regulators (the specific set depends on your sector).
Even though the specific standards vary by industry, procurement can still apply a consistent evaluation pattern derived from management-system thinking:
From a procurement perspective, these elements translate into contract requirements and vendor evidence requests. For instance, if the contract demands evidence-led compliance, the supplier must not only have procedures but also retain records demonstrating that the procedures were actually executed. Procurement can request the “proof chain” rather than only the “process description.”
In some industries, regulators require documented traceability for materials or processes. In those cases, the buyer’s contract acceptance criteria should align with regulatory expectations—especially regarding record retention and audit accessibility. Procurement should ensure that the supplier’s records can be accessed when needed, not only generated at shipment time. A common failure mode is suppliers who generate records but store them in formats or locations that prevent timely access during audits or customer requests.
Industry frameworks also help procurement establish scoring criteria. Instead of arbitrary vendor scoring, the buyer can score suppliers on the presence and quality of process documentation, evidence completeness, effectiveness of corrective actions, and robustness of change control. Such scoring is easier to defend and easier to standardize across categories.
Procurement should also consider the supplier’s maturity. A small supplier might not have a fully developed documented system comparable to a global enterprise, but they may have effective controls suitable for the scope. Therefore, procurement should tailor evaluation intensity while preserving evidence standards. The goal is to ensure compliance, not to force suppliers into a one-size-fits-all bureaucracy.
Even when sourcing is global, many organizations still evaluate certain constraints through a “nearby” lens—most commonly delivery reliability, regional compliance expectations, and communication responsiveness. If “city” or “country” context is included in the original keywords, it should be treated as “nearby” for this article’s framing.
In practical terms, buyers often prioritize:
This is especially important when evidence review cycles are short or when the procurement team must coordinate with quality, legal, and operations quickly.
“Nearby” framing can also reduce continuity risk. When suppliers are geographically closer, communication for change notifications and deviation handling may be faster, which increases the chance that evidence and operational actions remain aligned. However, procurement should not assume that proximity substitutes for evidence quality. A nearby supplier can still fail to document traceability properly or can have weak change control. Therefore, procurement should treat “nearby” as a factor in operational risk and responsiveness, not as a replacement for compliance proof.
In addition, regional differences may influence the way evidence is prepared. For example, document formats, signature practices, numbering schemes, and retention expectations can vary. Procurement should request evidence in formats that integrate with the buyer’s document review workflow. If the buyer has a strict records numbering or naming convention, procurement should provide a template or explicit guidance to avoid delays at review time.
Another “nearby” consideration is the feasibility of inspections. Where physical inspection is required, procurement can plan scheduling more easily with closer suppliers. If physical inspection is not feasible, procurement can rely more heavily on remote document audits, video witnessing, or third-party inspection certifications. In either case, the acceptance criteria should define what type of inspection evidence counts.
Finally, local communication and escalation pathways matter. Procurement should specify expected turnaround times for documentation clarifications and change notifications. For example, a supplier might be required to respond within a defined number of business days when documentation questions arise. Such requirements are particularly important when the supplier’s evidence review cycle intersects with production schedules.
| Component | Buyer expectation (objective) | What to request from the supplier | How to validate it |
|---|---|---|---|
| Cxxxvldlo definition | Clear mapping to requirements/specification lines | Specification interpretation note; scope boundaries; assumptions | Cross-check against contract deliverables and acceptance criteria |
| Pricing structure | Line-item consistency and auditable inclusions | Price breakdown; labor/material assumptions; compliance cost details | Normalize quotes to the same work breakdown; verify inclusions |
| Supplier evidence | Document control and traceability | Certificates, inspection results, batch/lot records, retention policy | Perform document completeness checks and selective review |
| Quality verification | Defined sampling/inspection methodology | Test methods; sampling plans; calibration records | Confirm methods align with requirements and are current |
| Change management | Controlled handling of process or material changes | Change control procedure; notification timeline; impact assessment format | Review past change records; test response scenario with a mock change |
To make the table more actionable, procurement teams can add “evidence required at which stage” as an internal note. For example:
This staged approach helps avoid the common trap where suppliers delay evidence until it is too late to correct gaps without causing schedule disruption.
The following step-by-step guide is designed to be repeatable across categories. Adjust the intensity and documentation depth based on the criticality of the scope and your regulatory environment.
To further strengthen the guide, procurement teams can implement “decision gates” aligned to these steps. Decision gates are formal moments when procurement moves from one phase to another (e.g., from RFQ to award) based on evidence thresholds.
For instance:
This gating prevents “silent” decisions where procurement proceeds despite missing evidence or unresolved interpretation. It also ensures that stakeholder involvement occurs when it matters most.
Another practical improvement is to define a “documentation response time” expectation. Suppliers sometimes provide evidence but take too long to respond when buyer reviewers request clarification. If the contract or PO requires evidence packages by a specific date, procurement should align it with an internal review schedule and define supplier response time for corrections. This reduces the risk of deadline overruns and schedule conflicts at receipt.
To treat Cxxxvldlo sourcing decisions as defensible, these conditions should be met:
In addition to these conditions, buyers should ensure that internal readiness is present. A procurement decision cannot be defensible if internal reviewers cannot interpret or validate the required evidence. Therefore, the buyer should confirm that the internal quality or engineering team has:
This internal readiness requirement may sound procedural, but it significantly affects outcomes. If the buyer cannot validate evidence, suppliers may become defensive, leading to more disputes and rework.
Buyers should also confirm that procurement documentation supports traceability and accountability. At minimum, purchase orders and contracts should include the relevant acceptance criteria, documentation requirements, and evidence submission timelines. If the contract lacks those items, Cxxxvldlo-related procurement can degrade into a negotiation after delivery—often the least favorable time to resolve compliance questions.
When those conditions are met, proceeding to award becomes a controlled step. When they are not met, procurement should either seek clarification before award, require a qualification/pilot stage, or restructure the contract to include compensating controls (e.g., additional testing at receipt, stronger audit rights, or delayed final acceptance pending evidence submission).
Cxxxvldlo is best understood as a procurement-and-compliance concept that indicates requirements, evaluation expectations, or process controls. In practice, teams should translate the term into specific contractual or technical requirements and define the evidence needed for verification.
Because the term is often used as an internal shorthand, the most valuable FAQ answer is operational: treat the term as a prompt to complete requirement interpretation and evidence mapping. If the organization cannot define what Cxxxvldlo requires in concrete terms, procurement should not proceed on assumptions.
Buyers should request a pricing breakdown aligned to the same scope definition and work breakdown structure. Then normalize quotes by separating compliance-related costs, logistics, labor, and optional items so that comparisons reflect the same deliverables.
In addition, buyers should confirm whether each quote includes evidence generation for each batch, whether retesting costs are included for nonconformities, and whether change-related revalidation activities are priced or treated as separate scope items.
Typically useful documents include certificates of conformity (where applicable), inspection and test records, traceability or batch/lot documentation, calibration records for testing tools, document retention/controls evidence, and a change control procedure with historical examples.
Procurement should also consider whether evidence is structured in a way that maps to buyer review needs. For example, batch records should reference the exact batch identifiers used in shipping labels and invoices. If there is a mismatch, evidence might be technically present but practically unusable during acceptance review.
Use a staged approach: start with documentation completeness checks and evidence mapping, then apply selective deep dives (e.g., sampled records) rather than attempting to audit every detail before initial qualification. High-criticality scopes can follow with pilot delivery verification.
This staged approach also helps avoid unnecessary delays. For example, if the supplier has a mature document control system, buyer reviews can focus on sampling and cross-checking rather than demanding full record sets upfront.
Buyers should clarify what is mandatory at award versus what can be delivered later (based on contract requirements). However, lack of evidence that is essential for acceptance criteria typically must be resolved before proceeding, or contractual controls should define compensating measures.
One practical mitigation is to define conditional acceptance: award can occur if the supplier can provide evidence references and demonstrate readiness, but final acceptance of deliverables depends on receiving the full evidence package. Another mitigation is to require a pilot lot before full rollout.
“Nearby” sourcing can reduce operational uncertainties such as lead time variability and communication delays, but compliance evaluation principles remain the same. The supplier still needs evidence and traceability aligned to the requirements.
Procurement can, however, adjust the verification modality: a closer supplier might allow easier on-site verification, while a distant supplier might require more remote documentation review and third-party certifications.
Yes. Organizations commonly align supplier quality and management expectations with internationally recognized standards (e.g., ISO management system concepts) and sector-specific regulatory guidance. For exact applicability, buyers should consult the relevant standards for their industry and jurisdiction.
However, procurement should treat standards as frameworks, not as replacements for contract-specific evidence mapping. The contract must translate standards concepts into explicit acceptance criteria and evidence requirements.
Even experienced teams can stumble. The most frequent pitfalls are:
Additional pitfalls that occur in real procurement environments include:
Each pitfall points back to the same root cause: lack of operational translation of the keyword into requirements, evidence mapping, and contractual controls.
When procurement avoids these pitfalls, the evaluation process becomes smoother because suppliers understand what the buyer is asking for and internal stakeholders can consistently validate submissions.
To operationalize this approach, procurement teams can adopt lightweight tooling even without complex software:
To expand these recommendations into a full workflow, procurement teams can also implement the following process elements:
A repeatable process should also define roles clearly:
When these roles are explicit, the team can reduce rework because decisions are made at the correct level and time. For example, engineering should resolve requirement interpretation ambiguities early, not after a supplier has already produced evidence packages.
Procurement can also improve repeatability by creating a “Cxxxvldlo library” internally. A library is not a collection of supplier secrets; it is a structured set of internal interpretations, mapping templates, evidence checklists, and standard language for contract clauses. Over time, the organization builds institutional knowledge, reducing the chance that each sourcing event starts from scratch.
Finally, it is useful to capture supplier performance feedback. If a supplier repeatedly provides incomplete evidence, procurement should record which evidence types are consistently missing and whether the gaps correlate with specific processes (e.g., subcontractor records, calibration traceability, or document revision handling). Supplier performance feedback can then inform future qualification intensity and contract requirements.
Cxxxvldlo-related sourcing succeeds when procurement teams treat keywords as a trigger for structured verification—clarifying requirements, comparing normalized pricing, and demanding evidence that supports compliance. By following a staged, evidence-first evaluation and by applying consistent conditions and requirements, buyers can reduce risk while improving decision speed and accountability.
When procurement operationalizes Cxxxvldlo through requirement mapping, evidence sufficiency standards, and pricing normalization, it creates an evaluation process that is understandable to suppliers and defensible to internal and external reviewers. It also reduces procurement’s dependence on subjective judgment. Instead of arguing about what a term might mean, procurement can focus on whether each requirement line has a corresponding proof point, whether documentation control is credible, and whether change management supports continuity of compliance.
Note: The keywords provided in the request included placeholders that could not be reliably interpreted as specific commercial product names or quantified pricing. This article therefore focuses on the defensible evaluation method you can apply whenever Cxxxvldlo (or similar sourcing/compliance terms) appears in procurement documentation.



Este guia ajuda você a avaliar produtos e fornecedores ligados ao termo “Opa”, organizando critérios práticos para comparar qualidade, origem e atendimento. Em seguida, você encontra um panorama objetivo sobre como esses termos costumam aparecer no mercado, quais riscos surgem quando a oferta é mal descrita e por que a rastreabilidade importa para a decisão de compra.
This guide explains Cxxxvldlo from a procurement and compliance perspective, focusing on how buyers evaluate suppliers, interpret pricing, and verify documentation. Background context is provided in an objective tone: the role of vendor qualification, typical risk controls, and why consistent standards matter when keywords like Cxxxvldlo and Cxxxvldlo-related requirements appear in real sourcing activities.
This guide explains how to evaluate O5176284516 in real purchasing workflows—covering supplier considerations, how pricing is typically formed, and what due diligence should look like. Objectively, O5176284516 functions as a reference code used to identify an item or procurement record, while supplier details and location context shape availability, lead times, and compliance expectations.
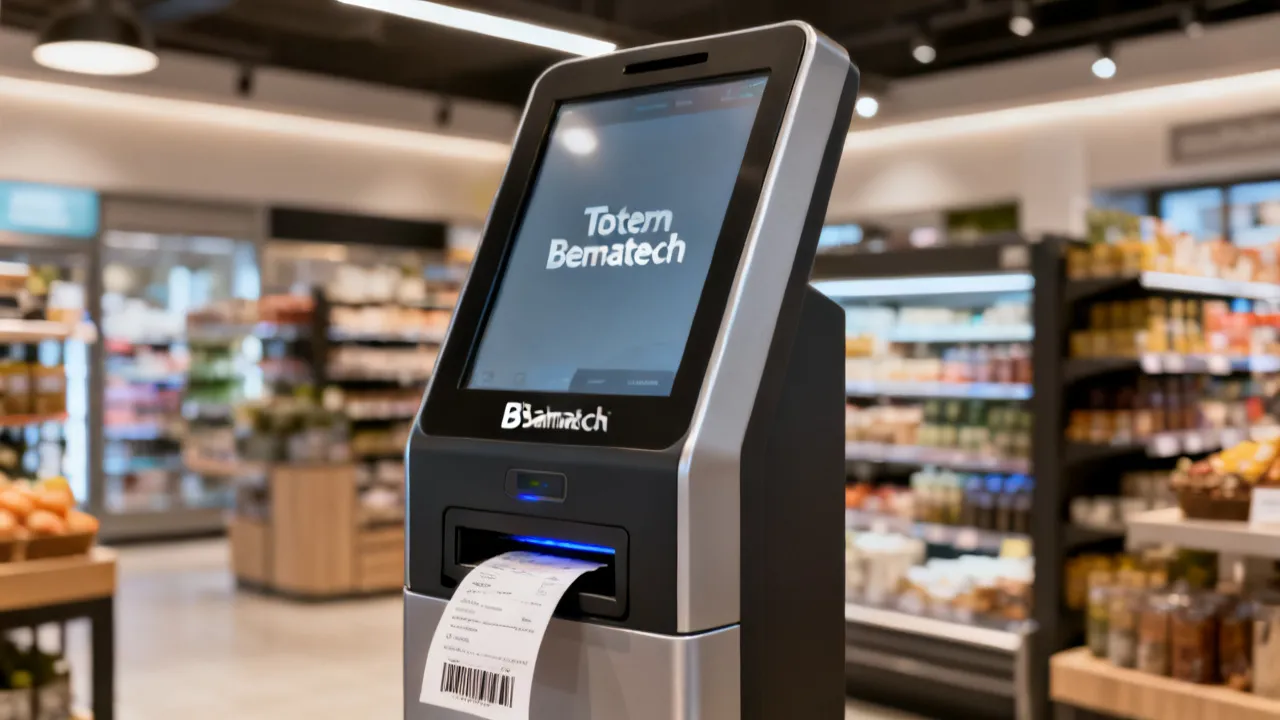
O Totem Bematech organiza e agiliza o fluxo de atendimento no varejo, integrando impressão, operação e experiência do cliente em um único ponto de uso. O guia apresenta, de forma objetiva, o que é um totem de autoatendimento, como ele se relaciona ao PDV e quais cuidados técnicos costumam orientar a escolha do equipamento e sua implantação.
This guide explains how to evaluate suppliers and procurement options tied to 03827516399, focusing on verifiable documentation, quality controls, and practical sourcing decisions. Background information is provided in an objective way around what such identifiers typically represent in procurement workflows, how compliance requirements reduce risk, and why structured comparison matters for good reliability.
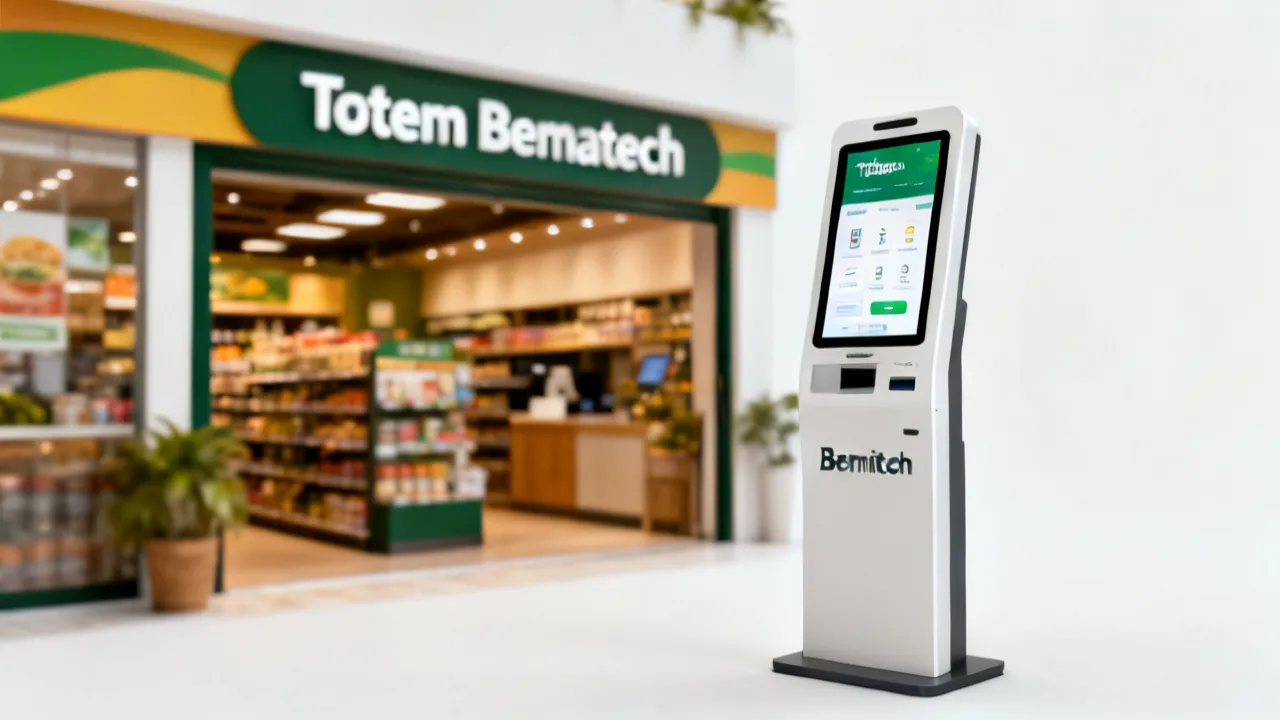
O Totem Bematech é um terminal de autoatendimento pensado para agilizar fluxos de atendimento e organizar informações ao cliente. Este guia descreve, de forma objetiva, o que envolve esse tipo de solução em operações varejistas e de serviços, abordando critérios de escolha, integração, manutenção e exigências práticas para implantação segura e eficiente.

