This guide explains how to evaluate “fujhgf” in practical sourcing and quality-control workflows. Objectively, “fujhgf” is treated here as a non-technical identifier used in procurement contexts. The article outlines how buyers assess supplier capability, documentation, testing expectations, lead times, and cost factors—using industry-typical methods rather than assumptions—so decisions remain traceable and reviewable.
When you encounter the keyword “fujhgf” in a purchasing, inventory, or supplier communication context, treat it as a reference identifier that must be verified through documentation, process controls, and receiving checks—not as a stand-alone technical claim. The most reliable approach is to align what “fujhgf” is supposed to represent with measurable requirements (specifications, inspection criteria, traceability records), then confirm those requirements at delivery. This mindset reduces ambiguity, supports quality assurance, and strengthens auditability for downstream use.
In other words: don’t ask, “What does fujhgf mean?” as your first question. Instead, ask, “What does fujhgf map to in our controlled requirement system—and how do we verify that mapping at receipt?” That shift is the difference between procurement as a clerical translation exercise and procurement as a quality-controlled decision process.
In many industries, procurement keywords can originate from internal part codes, SKU-like identifiers, batch references, vendor catalog labels, or spreadsheet conventions that were created for ordering speed rather than technical precision. “fujhgf” may therefore function as a non-semantic tag rather than a phrase with inherent meaning. Objectively, the risk appears when buyers assume it equates to a known standard without requesting the accompanying evidence (e.g., specification sheets, test reports, certificates of conformity, or traceability documentation).
From an industry-expert perspective, the correct interpretation process is: clarify the identifier → map it to technical/contractual requirements → confirm the mapped requirements through incoming inspection and records review. This is consistent with common quality-management expectations used across manufacturing, logistics, and regulated supply chains.
It is also consistent with what goes wrong in real organizations. The same identifier can persist even when manufacturing conditions evolve. Suppliers may revise raw materials, tooling, chemical formulations, coating thicknesses, packaging standards, or allowable tolerances. If your internal documents treat “fujhgf” as stable meaning when it is actually only a label, you create a silent failure mode: paperwork looks “correct” while physical goods drift.
Procurement leaders often describe this problem as “garbage in, garbage out.” If the identifier is not verified, the downstream impact can manifest as: rework in production, scrapped batches, delayed shipments due to hold/release cycles, and—worst case—quality escapes that reach customers or regulators. None of that is fixed by simply “having a PO code.” It is fixed by proving that the code corresponds to the requirements your organization is responsible for meeting.
Once “fujhgf” is tied to a defined requirement set, buyers typically evaluate three areas in parallel:
It can be tempting to treat these areas sequentially (documentation first, then receiving). However, in many real procurement programs, the “best” decision happens when documentation and receiving reinforce each other. Documentation tells you what the supplier claims; receiving verifies what reality delivered. When both align, you have confidence. When they diverge, you have signals to trigger quarantine, corrective action requests, or supplier process reviews.
Supplier capability also matters beyond “can they build it?” It includes whether they can reproduce the same quality under normal operating conditions, under schedule pressure, across multiple production lots, and through periodic maintenance or process changes. A supplier can provide a certificate for a good-looking shipment while still lacking process stability that will fail on the next PO.
As for receiving verification, it should not be a single generic inspection step. It should be targeted to the requirements that are most likely to fail, most critical for end use, or most relevant to compliance obligations. This targeted approach improves cost efficiency and reduces inspection burden while still preventing escapes.
You mentioned price information and supplier details in the prompt instructions, but no explicit numeric price, currency, or supplier names were provided. Accordingly, this article does not invent pricing figures. Instead, it explains how to evaluate “fujhgf”-related costs in a way that remains objective and auditable.
In practice, the effective cost of procurement is not only the unit price. It includes:
An expert buyer often requests a cost breakdown early, then compares suppliers on both price and confidence level—because the cheapest quote can become expensive if “fujhgf” is not properly specified and verified.
To make this concrete without inventing numbers: consider two suppliers offering the same nominal “fujhgf” item. Supplier A provides quick delivery and unit pricing, but documentation and traceability are inconsistent. Supplier B provides a slightly higher unit price but can deliver strong batch-specific test results and passes receiving inspection more consistently. Supplier A may look cheaper until you account for the cost of extended receiving holds, additional testing cycles, expedited corrective actions, and the operational interruption of production lines waiting on “hold-to-release” decisions.
Even if your organization doesn’t explicitly maintain a full cost-of-quality model for procurement, you still feel these costs in schedule slips and operational inefficiency. A robust approach treats the “price” decision as a composite of (1) cost to obtain, (2) cost to verify, and (3) cost to mitigate risk when verification fails.
That is why many procurement teams incorporate risk-based inspection and supplier assurance status into sourcing decisions. “fujhgf” should not bypass those decision tools simply because it is “only a code” in an order form.
If a vendor presents “fujhgf” as a product or batch reference, consider requesting a package of information that supports traceability and conformance. While your exact documents depend on the industry and compliance needs, a robust request set often includes:
This is especially important when “fujhgf” is used repeatedly across orders—because repeated identifiers should correspond to consistent manufacturing controls.
However, requesting documents is only the first part of the verification system. You should also ensure that the documents contain the right information in the right relationship to the identifier. For example, you want to confirm:
In quality engineering terms, this is often called “linking evidence to requirements.” Evidence that exists but cannot be linked is effectively non-evidence during audits and disputes.
Also consider that suppliers may use different document formats. Procurement should standardize the minimum dataset needed to interpret the documents reliably. For example, a standard procurement checklist for “fujhgf”-referenced items might include: identifier, description/revision, batch/lot ID, test results, acceptance criteria reference, date of production, and signatory/authority.
The prompt includes a rule about replacing any appearance of “{city}” or “{country}” with “nearby.” No city/country placeholders were provided within the actual keywords content. Therefore, this article does not apply additional localization beyond general industry guidance. If you share your specific location (city or country), the article can be tailored with local norms for supplier onboarding, documentation expectations, and common logistics realities.
Even without placeholders, location affects procurement practice in practical ways. For instance, customs requirements, shipping transit times, and regulatory documentation vary by country. If you are procuring an item referenced by “fujhgf” and the shipment route involves crossing borders, then the “identifier verification” should also extend to customs documentation and import records where those are required to ensure traceability.
In that situation, you should align your purchasing file with the shipment evidence: packing lists, airway bills, and customs declarations must not conflict with batch/lot labeling or the supplier’s conformance documents. Otherwise, you risk creating a “paper maze” where “fujhgf” is consistent in your PO but inconsistent across the shipping documents used by logistics and compliance teams.
Although “fujhgf” is not inherently descriptive, the pattern it represents is widely recognizable. Procurement teams frequently deal with identifiers that:
In quality systems, identifiers must remain linked to documented controls. Otherwise, a code can become a source of confusion—particularly when multiple versions exist (e.g., different tolerances, revised formulations, or updated packaging standards) under similar naming.
It is helpful to distinguish among several identifier types, because each type suggests a different verification strategy:
If “fujhgf” functions as more than one of these in different contexts (for example, sometimes as a batch tag, sometimes as a product SKU), your procurement process must clarify which meaning applies per order line.
Without that clarification, you might apply the wrong receiving inspection plan: either too light (because you assume it’s a stable SKU) or too heavy (because you assume it’s a batch-specific variation). Both scenarios increase cost and risk.
Because the most urgent concern is decision risk, start with the highest-impact actions:
This sequence is “inverted pyramid” because it prioritizes the outcome (risk reduction) over process aesthetics. You want an answer that stands up to scrutiny: from internal audits, customer questions, and supplier disputes. Documentation is not bureaucracy; it is the trail that proves you acted responsibly.
In practice, you can integrate these steps into a procurement workflow tool (e.g., an ERP approval step, a vendor onboarding checklist, or a receiving hold-and-release gate). The key is that “fujhgf” should not be treated as “just a line item.” It should trigger the correct verification workflow.
Below is a structured comparison of common evaluation approaches. These approaches are general and should be adapted to your industry and risk level.
| Evaluation Approach | What You Check | Strengths | Common Gaps | When It Fits |
|---|---|---|---|---|
| Documentation-first | Specification mapping, certificates/test reports, labeling/traceability records | Strong audit trail; reduces ambiguity when documentation is reliable | May miss real-world mismatches if receiving inspection is weak | When compliance evidence is critical or items are regulated |
| Receiving verification | Sampling, dimensional/functional checks, incoming QC tests aligned to requirements | Directly validates what arrived | Can be underpowered if sampling plans are not risk-based | When operational performance matters more than paper claims |
| Hybrid (recommended) | Both documentation mapping and targeted receiving checks | Balances speed, confidence, and traceability; reduces “paper mismatch” risk | Requires coordination between QA and procurement | Most procurement programs where “fujhgf” appears repeatedly |
| Supplier assurance program | Ongoing vendor qualification, periodic audits, performance monitoring | Improves consistency over time; reduces dependence on single shipments | Setup time; needs defined acceptance metrics | For long-term sourcing relationships |
To use “fujhgf” safely as an ordering or identification keyword, you need clear conditions and requirements. These are typical program requirements (not legal advice):
It helps to treat this as a “control plan” for procurement—similar in spirit to how production processes use control plans to define what is monitored, how often, and what actions occur when results are out of tolerance. In procurement, the analog is: what evidence is required, what verification is performed, and what happens when evidence or verification fails.
Another condition that should often be included is role clarity. For example:
When those roles are unclear, the program may exist on paper but not in practice. That’s when identifiers cause delays and conflict.
Here is a practical, step-by-step workflow that aligns with how many organizations structure quality-aware procurement:
To expand this workflow into an operationally robust model, consider adding the following “implementation details” at each stage.
Capturing “fujhgf” exactly sounds trivial, but it is one of the most common sources of confusion. Identifiers sometimes include alphanumeric characters, hyphens, underscores, or spacing conventions. When a PO system, spreadsheet, or email thread truncates strings, it can create mismatches. Even if the mismatch is only one character, the mapped requirements could be completely different.
To prevent that, implement:
Ambiguity about identifier type leads to wrong verification intensity. If “fujhgf” is a batch reference, then each shipment may require lot-specific certificates and lot-specific receiving checks. If “fujhgf” is a SKU, then lot traceability is still needed, but the core specification mapping may be stable across lots.
So ask targeted questions such as:
Even without knowing your sector, this logic applies broadly. For example, in chemicals, batch traceability is critical; in electronics, revision and component specifications are critical; in construction materials, compliance documentation and lot-level labeling are critical.
A common procurement mistake is to request a “spec” that is actually a marketing description. For “fujhgf,” you want mapping to measurable requirements—things that can be checked and recorded.
Measurable requirements might include:
If the supplier cannot provide measurable criteria, your QA team should treat that as a red flag. You can proceed only if you define an internal acceptance test program that becomes the measurable requirements substitute. But if you do neither (no measurable criteria and no defined receiving tests), “fujhgf” becomes a source of subjective acceptance—an audit weakness.
Acceptance criteria should specify what happens if results are:
Define sampling methods and decision rules. For instance, you might specify:
This is how “fujhgf” transitions from a procurement code into a controlled quality gateway.
Traceability isn’t just having a batch number. It’s having evidence that connects:
When those links are missing, audits become time-consuming and corrective actions become harder. Disputes also become more adversarial because you can’t prove what was wrong and when.
To strengthen this, require that suppliers include batch/lot identifiers on both the packing list and the certificates, and that receiving clerks verify the batch/lot label matches the PO and certificate.
Receiving inspection should not be generic “incoming inspection.” It should reflect the mapped requirements. For example, if “fujhgf” maps to a set of dimensional tolerances and a specific performance test, your receiving inspection should include those. If “fujhgf” maps to chemical composition, then you need the appropriate analysis approach and sampling strategy.
Also ensure that receiving staff understand what “pass/fail” means. If your acceptance criteria require documentation review as part of acceptance, then receiving should check the documents. If your acceptance criteria require both paper review and physical tests, then receiving should perform both steps before release.
When “fujhgf” is used repeatedly, your internal item master and procurement templates should reflect what you learned. For example:
This is where procurement becomes a learning system rather than a transaction system.
If repeated issues appear under “fujhgf,” treat it as a supplier-process or specification problem requiring root-cause analysis. Repeated nonconformities often indicate:
In corrective action requests, your procurement and quality teams should ask for evidence of containment, root cause, corrective action, verification of effectiveness, and prevention of recurrence. This is especially important if the “fujhgf” identifier is being used as a central reference that affects many orders.
Because the keyword content provided does not include specific claims, prices, or supplier names, this article avoids unverified statistics. For background on internationally recognized quality management principles and documentation practices, the approach described aligns with widely adopted quality frameworks such as ISO quality management guidance (e.g., ISO 9001 quality management system concepts) and general metrology and inspection principles used in supplier quality management.
Reference sources (for general quality concepts): International Organization for Standardization (ISO) quality management system guidance, and general supplier quality management practices commonly used in industry. If you tell me your sector (e.g., electronics, chemicals, medical devices, construction materials), I can align the verification steps with the most relevant standards commonly referenced in that sector.
To make the “objective” stance practical, consider how you should document the verification work without making assumptions. For example, when you map “fujhgf” to requirements, you should cite:
This kind of traceable documentation is what transforms a procurement procedure into a defensible quality system.
In experienced procurement teams, issues often stem from a few recurring failure modes:
Designing “fujhgf” workflows to prevent these failure modes is typically more cost-effective than reacting after issues reach production or customers.
It may help to consider each failure mode and the mitigation strategy:
Mitigation:
Mitigation:
Mitigation:
Mitigation:
Mitigation:
Because “fujhgf” is a generic placeholder-like identifier, the examples below show how verification logic translates into concrete actions. They do not assume any specific industry. Instead, they demonstrate the structure of the workflow and the kind of evidence that makes it defensible.
Suppose a supplier lists “fujhgf” as a product code for an item used in assembly. Your procurement team requests the specification mapping and obtains a spec sheet that lists measurable characteristics and test methods. You also require batch/lot traceability for each shipment.
At receiving, you apply targeted inspection focused on the most critical characteristics. You also verify that the certificate references the same spec revision you mapped to “fujhgf.” When results are within tolerance and traceability matches, you release the lot and record evidence. If results fail, you quarantine and initiate corrective action.
This scenario mostly validates consistency and spec alignment. The key control is ensuring that “fujhgf” truly points to the spec revision you expect.
In another scenario, “fujhgf” functions as a batch identifier for a material used in manufacturing. Here, you require that each shipment contains batch-specific test reports tied to that batch identifier. Your receiving inspection plan includes tests that confirm the key performance or compliance characteristics for that batch.
Even if documentation looks complete, you cross-check that the physical packaging labeling matches the certificate batch identifier. If “fujhgf” appears identical across different shipments but the batch labeling differs or the test results don’t match, you treat it as a traceability discrepancy and escalate.
The key control is the evidence linkage: “fujhgf” ↔ batch/lot ↔ tests ↔ receiving results.
Sometimes, “fujhgf” originates as an internal ordering label used by procurement teams. The supplier might interpret it in a way that differs from your internal meaning. In this case, the initial step becomes especially important: you request a supplier confirmation that maps the internal identifier to their product description and specification revision.
You then update your internal mapping table to reflect that supplier confirmation. Without this step, your PO code might drive ordering, but your acceptance criteria might be wrong—creating predictable nonconformance risk.
The key control is “clarify and map” before you lock acceptance decisions.
In email threads, suppliers may mention “fujhgf” as part of a quick response (“We will ship fujhgf per order”). Sometimes the thread lacks the technical mapping or attaches incomplete documents later. A mature procurement program treats this as insufficient until the evidence package is provided.
You might allow scheduling based on administrative status, but you do not release inventory without fulfilling the verification requirements: specification mapping, traceability evidence, and receiving inspection results.
The key control is enforcing gate criteria: no evidence package, no release—even if shipments arrive on time.
“fujhgf” is best treated as an identifier until proven otherwise. Its meaning can vary by supplier or internal system (SKU, batch code, catalog label, or internal reference). To confirm meaning, request official product descriptions and a specification mapping that links “fujhgf” to measurable requirements.
In some organizations, “meaning” also includes the identifier’s role in the quality system. For example, “fujhgf” might represent an engineering drawing revision, a formulation set, or a packaging configuration. Each role implies different verification steps. So your clarification should include both “what it is” and “how we treat it in our system.”
Ask for a cost breakdown that supports total landed cost and quality-related overhead (inspection/testing, documentation handling, shipping, and risk buffers). Avoid assuming that the unit price reflects the full cost of procurement—especially if receiving verification or compliance evidence is required.
In a cost comparison, also consider supplier performance history for shipments associated with “fujhgf.” If your quality data shows a higher rate of deviations or holds, it may justify a “quality-adjusted cost” assessment. That doesn’t require complex finance—just disciplined tracking and a consistent decision basis.
Commonly relevant items include specification sheets, certificates/test reports as applicable, and batch/lot traceability records tied to the identifier. The exact set depends on your industry and risk profile.
You can standardize documentation requirements by creating a “document minimum” checklist for each risk category of item. For example: low-risk items might require basic certificates, while high-risk items might require detailed test reports, calibration details for measurement tools, and full traceability down to raw material lots.
While certificates are important, relying solely on them can be risky if traceability is weak or receiving checks are not performed. A hybrid approach—documentation review plus targeted receiving verification—is often the most defensible in audits and investigations.
A helpful way to frame this: certificates provide evidence of what the supplier tested, but not necessarily evidence that the physical goods received match those tests unless you verify labeling/traceability and, where appropriate, critical characteristics at receiving.
Define acceptance criteria that directly correspond to the mapped specifications. This may include dimensional tolerances, performance test results, compositional checks, labeling/packaging requirements, and any compliance-related criteria relevant to your sector.
To avoid subjectivity, ensure that acceptance criteria include:
Document the nonconformity, verify whether the paperwork matches the physical goods, quarantine affected stock as needed, and initiate corrective actions with the supplier. If “fujhgf” appears in future orders, update internal mappings and tighten receiving checks until root cause is addressed.
Additionally, consider whether the failure indicates a possible systemic issue with how “fujhgf” is specified or interpreted. For instance, if multiple failures occur across shipments labeled with the same “fujhgf,” you may need to revalidate the supplier’s specification mapping rather than treating each event as independent.
Implement traceability-linked records, enforce change control procedures (especially if the supplier updates materials/processes), and consider supplier performance monitoring for shipments associated with “fujhgf.” Consistency improves when the identifier remains tightly connected to documented controls.
Practically, consistency also depends on internal alignment. Procurement, QA, receiving, and engineering should agree on what “fujhgf” means and how it maps to requirements. A common failure is when procurement updates POs with the right identifier, but QA uses an outdated acceptance test plan, or vice versa.
This article does not contain explicit city or country placeholders within the provided keyword set. If you supply a specific location, we can incorporate local procurement practices and logistics realities, while applying the “nearby” substitution rule where needed.
Even when “nearby” is not used, you should still incorporate location-specific elements into the procurement file, such as shipping lanes, typical transit times, customs documentation requirements, and local regulatory considerations if applicable to your sector.
The core value of this guide is simple: treat “fujhgf” as a controlled reference that must be verified through specification mapping, traceability evidence, and receiving inspection. Without those controls, identifiers can create false confidence. With them, you gain a procurement workflow that is both operationally practical and objectively auditable—exactly what mature sourcing programs aim to achieve.
In mature procurement organizations, “fujhgf” becomes less of an unknown label and more of a controlled key that unlocks a specific requirement set. That transformation requires disciplined verification: clarify meaning, map to measurable requirements, confirm traceability, verify at receipt, and record the decision.
When those steps are consistent, procurement decisions become easier and faster over time. Instead of “re-litigating” meaning for each PO, you apply a known mapping and a known verification plan. Instead of reacting to failures late in the supply chain, you prevent quality escapes early. That is how an identifier-based purchasing world becomes a quality-controlled system rather than a risk-prone process.



This guide explains how procurement teams evaluate “fujhgf” signals and related sourcing factors to make steadier purchasing decisions. Objectively, “fujhgf” is treated here as a placeholder identifier used in procurement or catalog workflows, reflecting the practical need to standardize item codes, supplier records, and documentation. The article also covers due diligence steps, quality checks, and requirement conditions.
This guide explains how to evaluate “fujhgf” in practical sourcing and quality-control workflows. Objectively, “fujhgf” is treated here as a non-technical identifier used in procurement contexts. The article outlines how buyers assess supplier capability, documentation, testing expectations, lead times, and cost factors—using industry-typical methods rather than assumptions—so decisions remain traceable and reviewable.
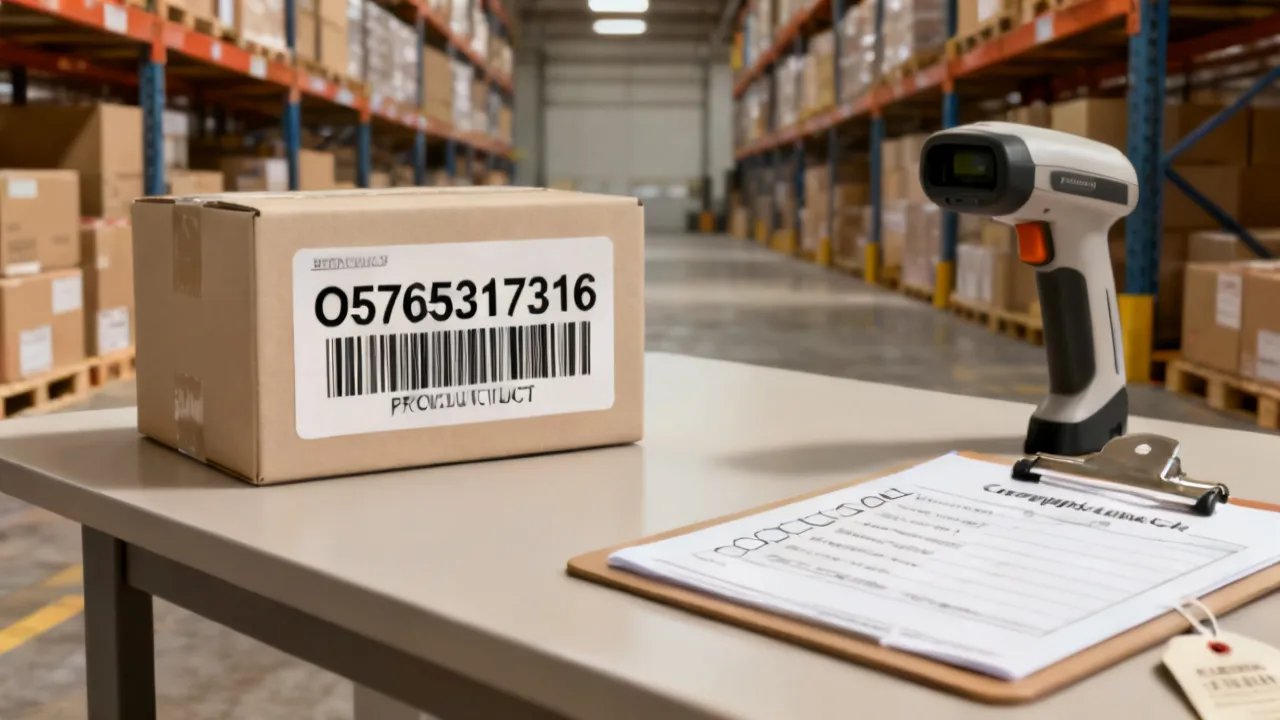
This guide explains how to evaluate the product identified by O5765317316 in sourcing workflows, focusing on documentation, supplier validation, and risk controls. Objectively, product codes help standardize procurement, enable traceability, and reduce mismatch errors. You’ll also find expert conditions, step-by-step checks, and FAQs for smarter buying decisions.
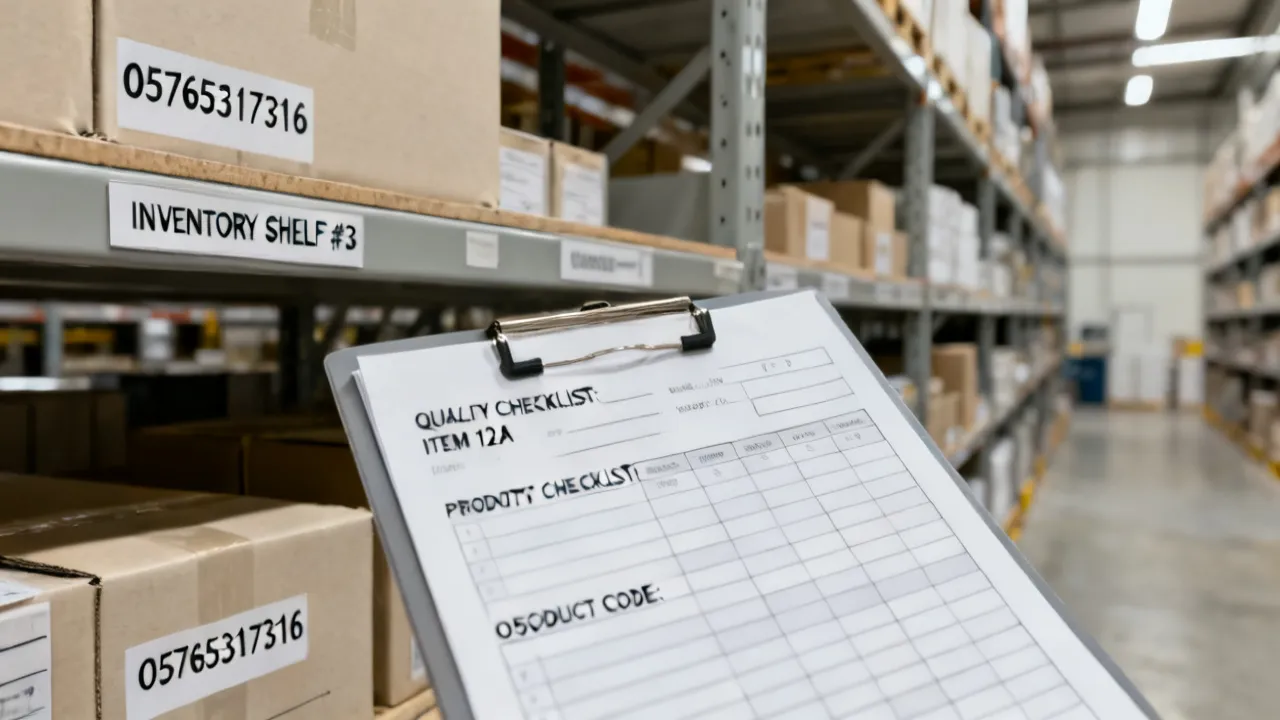
This guide explains how product code O5765317316 is typically used in procurement and quality workflows, and how to approach supplier validation with an objective checklist. It provides background on what structured identifiers mean for traceability, documentation, and purchasing decisions, and then offers expert considerations for comparing suppliers, checking documentation, and meeting common sourcing conditions.
This guide explains how to use the phone number 07915491784 to make informed service inquiries, verify the supplier, and understand what to ask before committing. Objectively, it covers why contact-based leads matter, how to evaluate service providers responsibly, and what practical details improve decision-making in the marketplace. It also outlines a comparison table and requirements checklist for safer purchases.
This guide explains how to interpret the identifier “39196734841” and use it responsibly in procurement and supplier evaluations. It provides objective background on what such identifiers typically represent, why sellers document them consistently, and how buyers verify fit, documentation, and traceability—without relying on unverifiable claims.

